Author
SecurityXP
115 articles published · Page 3 of 6 RSS feed

SecurityXP delivers cybersecurity news, vulnerability analysis, data breach reports, and threat intelligence.
Articles
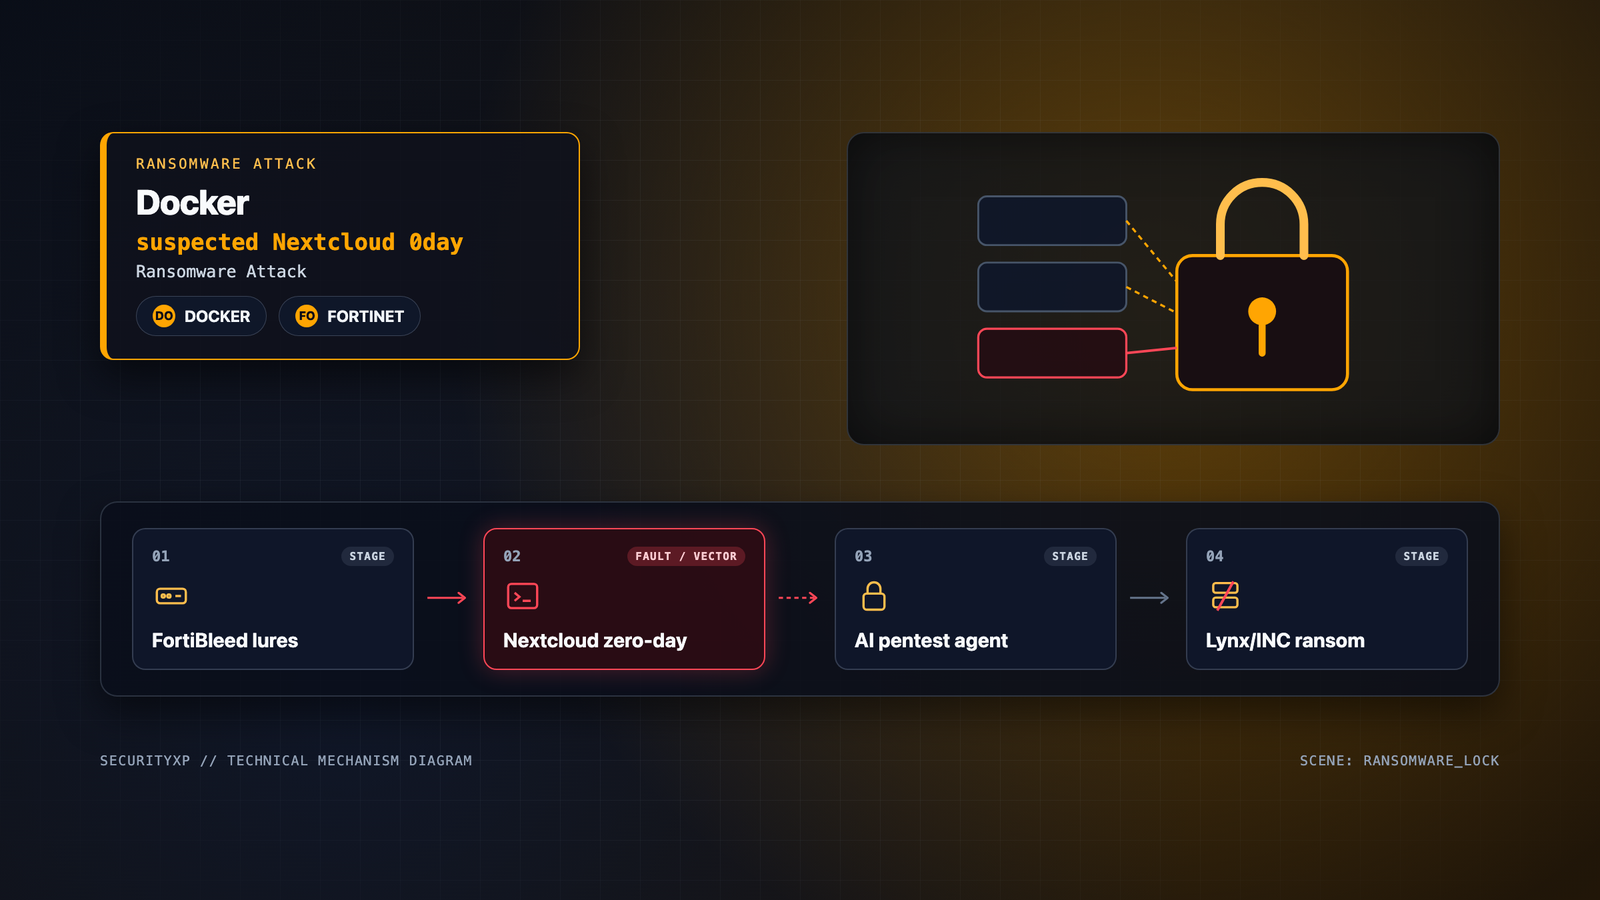
115 totalSOCRadar links FortiBleed campaign targeting manufacturers to Lynx and INC ransomware attacks
The hacker likely already found and exploited a zero-day vulnerability in Nextcloud, an open-source content collaboration platform. They also built ‘PENTEST...
Beyond safety and security: Why automotive open source demands dependability
Bridging the gap between the upstream velocity of Linux and the downstream rigor of automotive standards requires more than just a repository: it requires a...
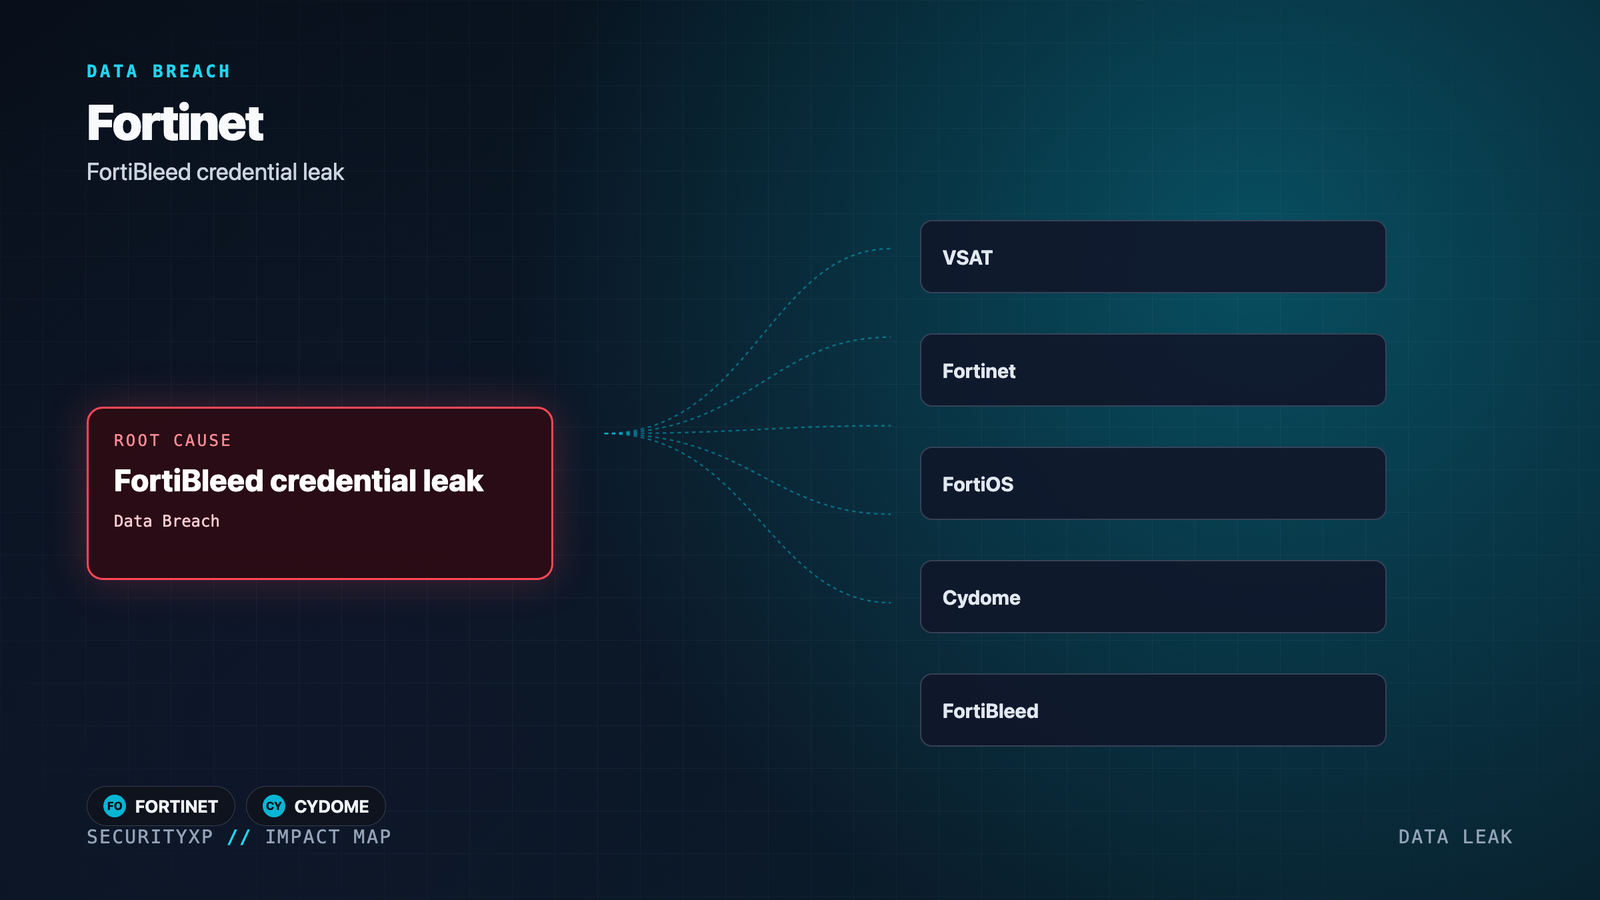
Cydome reports FortiBleed credential leak poses elevated risks to maritime and energy critical infrastructure
On a vessel without clean IT and OT separation, that same path can reach bridge systems, cargo management, and VSAT links.” Fortinet officially characterizes...
Critical Adobe ColdFusion Vulnerability Exploited in Attacks (CVE-2026-48282)
However, according to the vulnerability intelligence platform KEVIntel, hackers began exploiting CVE-2026-48282 within two hours of its public disclosure...
OpenAI Codex Desktop App for macOS Vulnerability Allows Attackers to Inject Indirect Prompt
As AI-assisted development tools continue to gain adoption, vulnerabilities like CVE-2026-14898 underscore the need for secure design practices that account...
Threat Modeling Generative AI: What 11,658 Incidents Reveal About Real-World Risk
Instead, improper output handling (42%) and misinformation/misuse (35%) represent the vast majority of actual incidents.
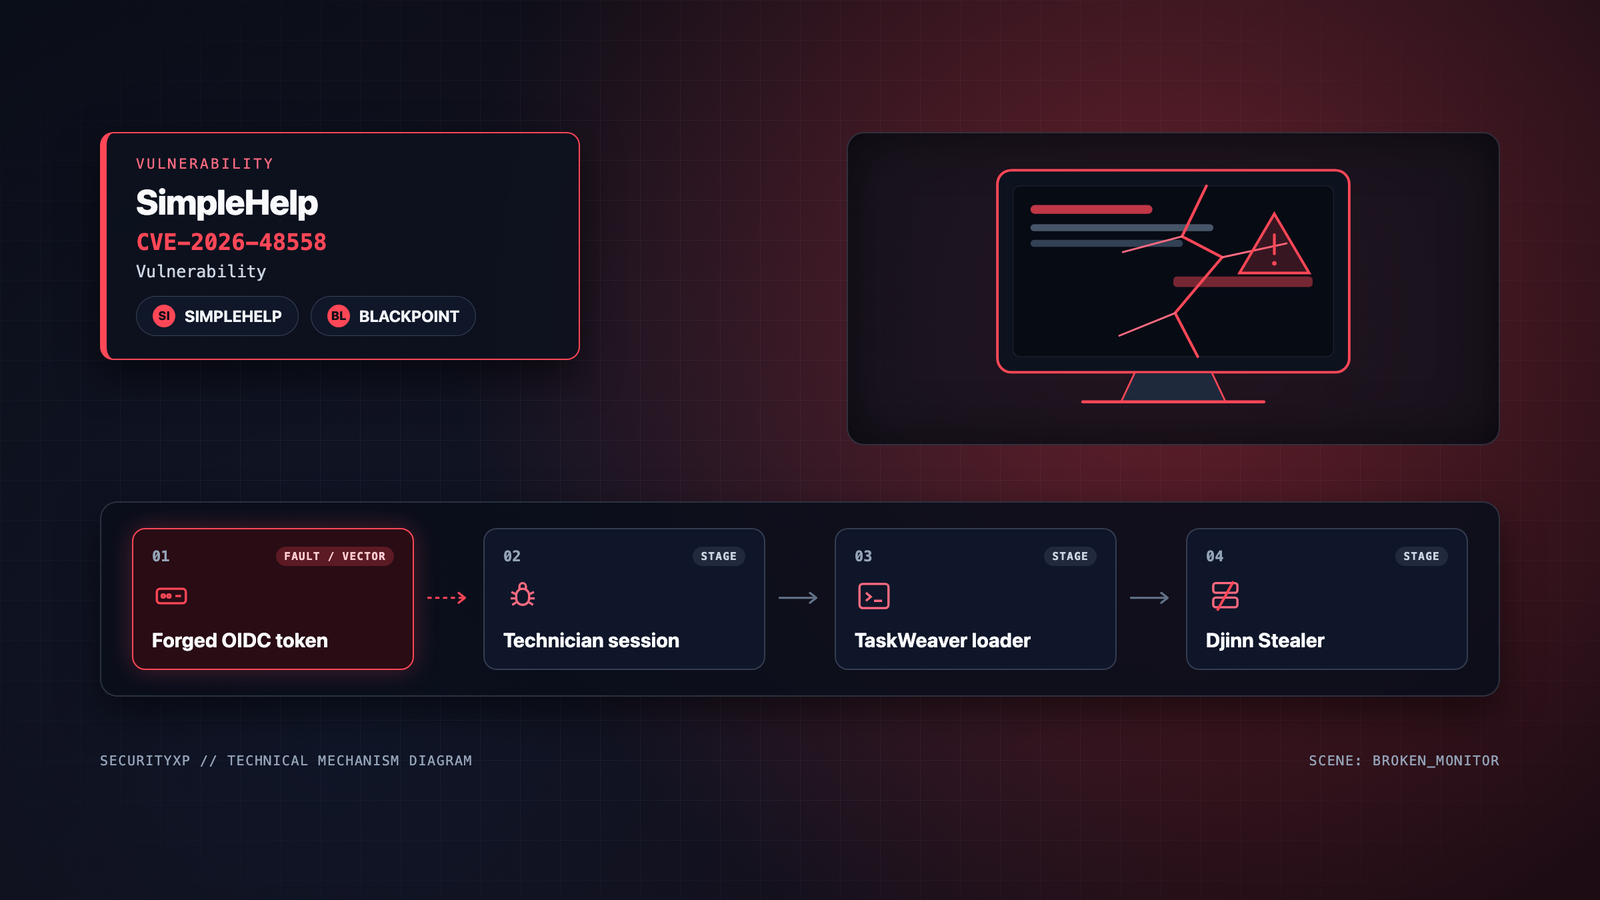
Attackers Exploit SimpleHelp CVE-2026-48558 to Deploy TaskWeaver and Djinn Stealer
"Credentials accessible from a developer or administrator workstation may provide entry into production infrastructure, build pipelines, source code...
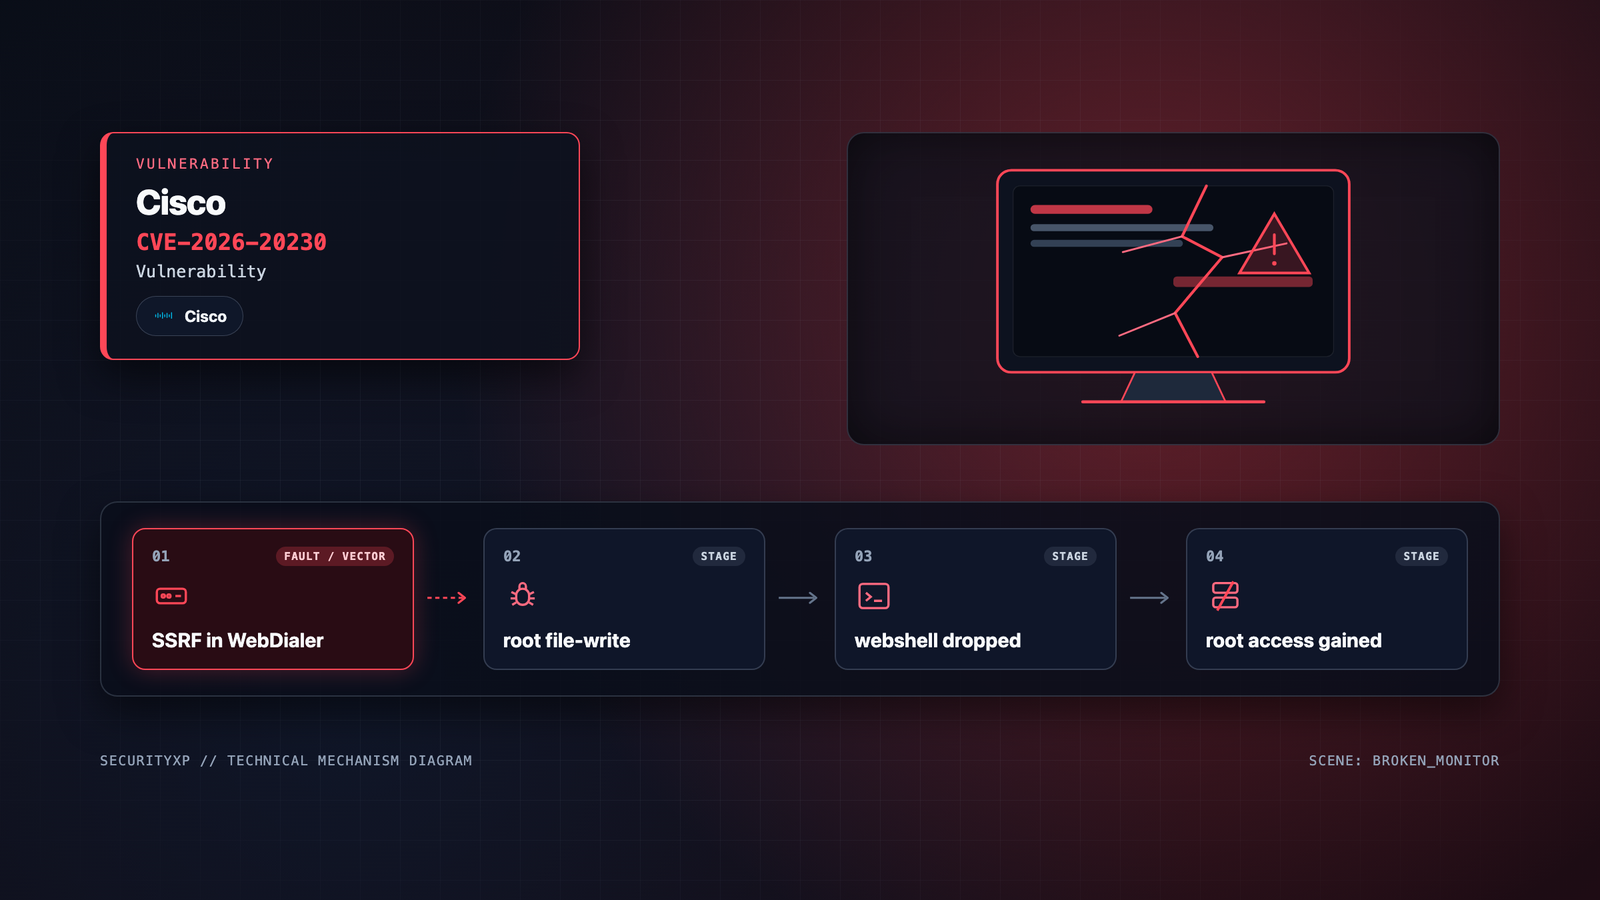
Cisco Unified CM Flaw CVE-2026-20230 Actively Exploited in the Wild
Cisco Unified Communications Manager has a serious vulnerability, tracked as CVE-2026-20230 (CVSS score of 8.6), that attackers are already exploiting. The...
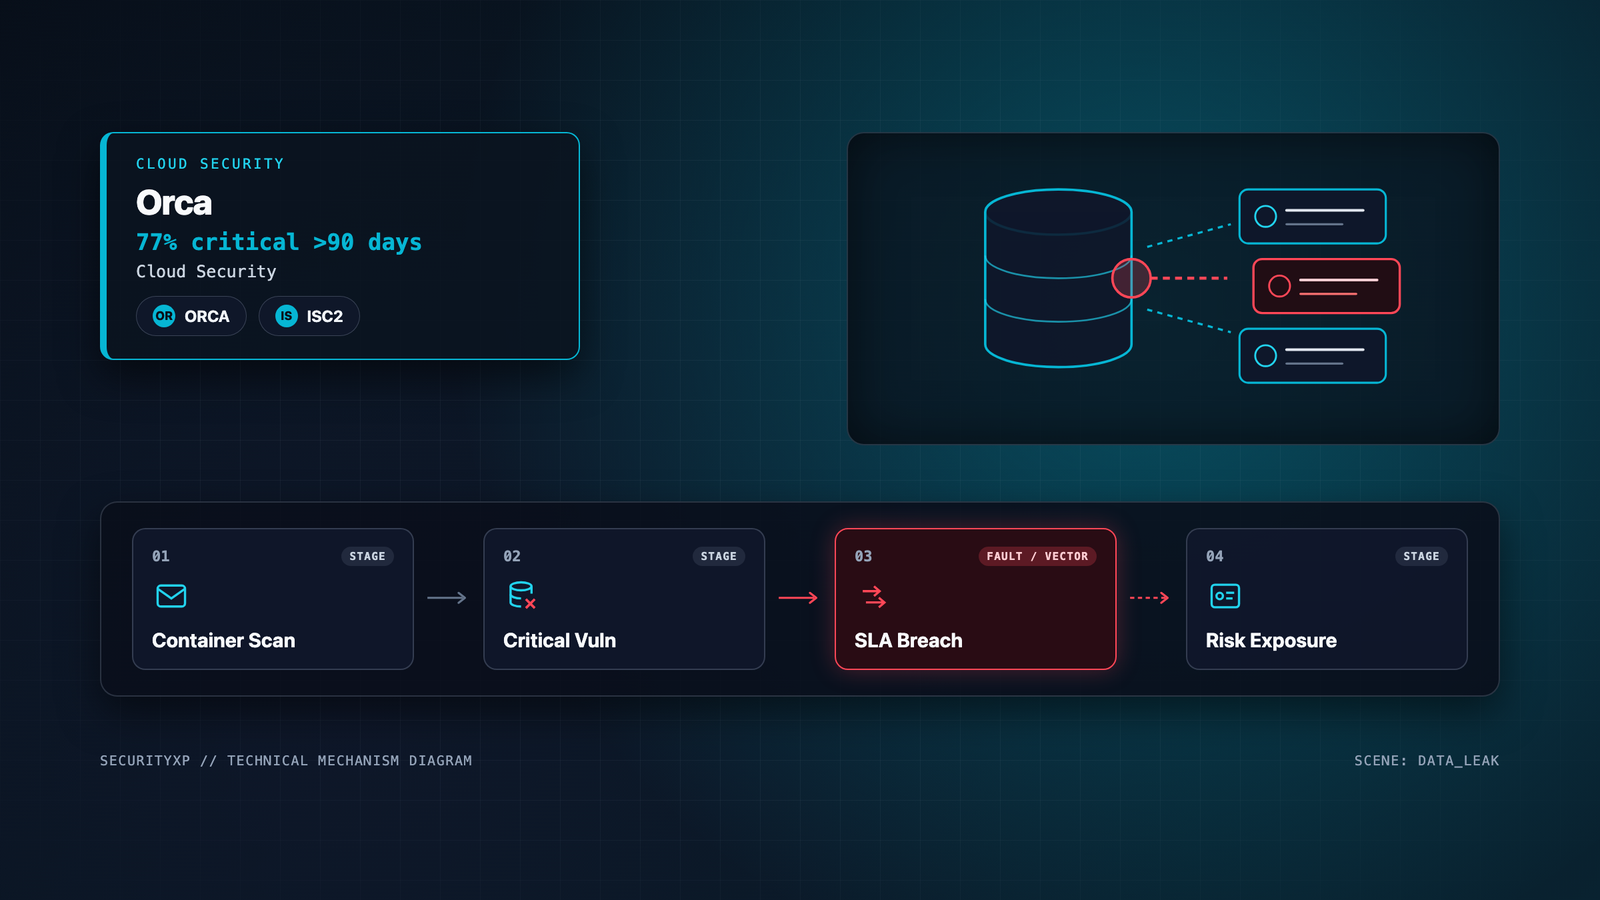
From Platform to Program: How to Ensure Your Cloud Security Solution Delivers
Orca’s 2026 State of Application Security Report found that 77% of organizations retain high or critical container vulnerabilities for more than 90 days, a...
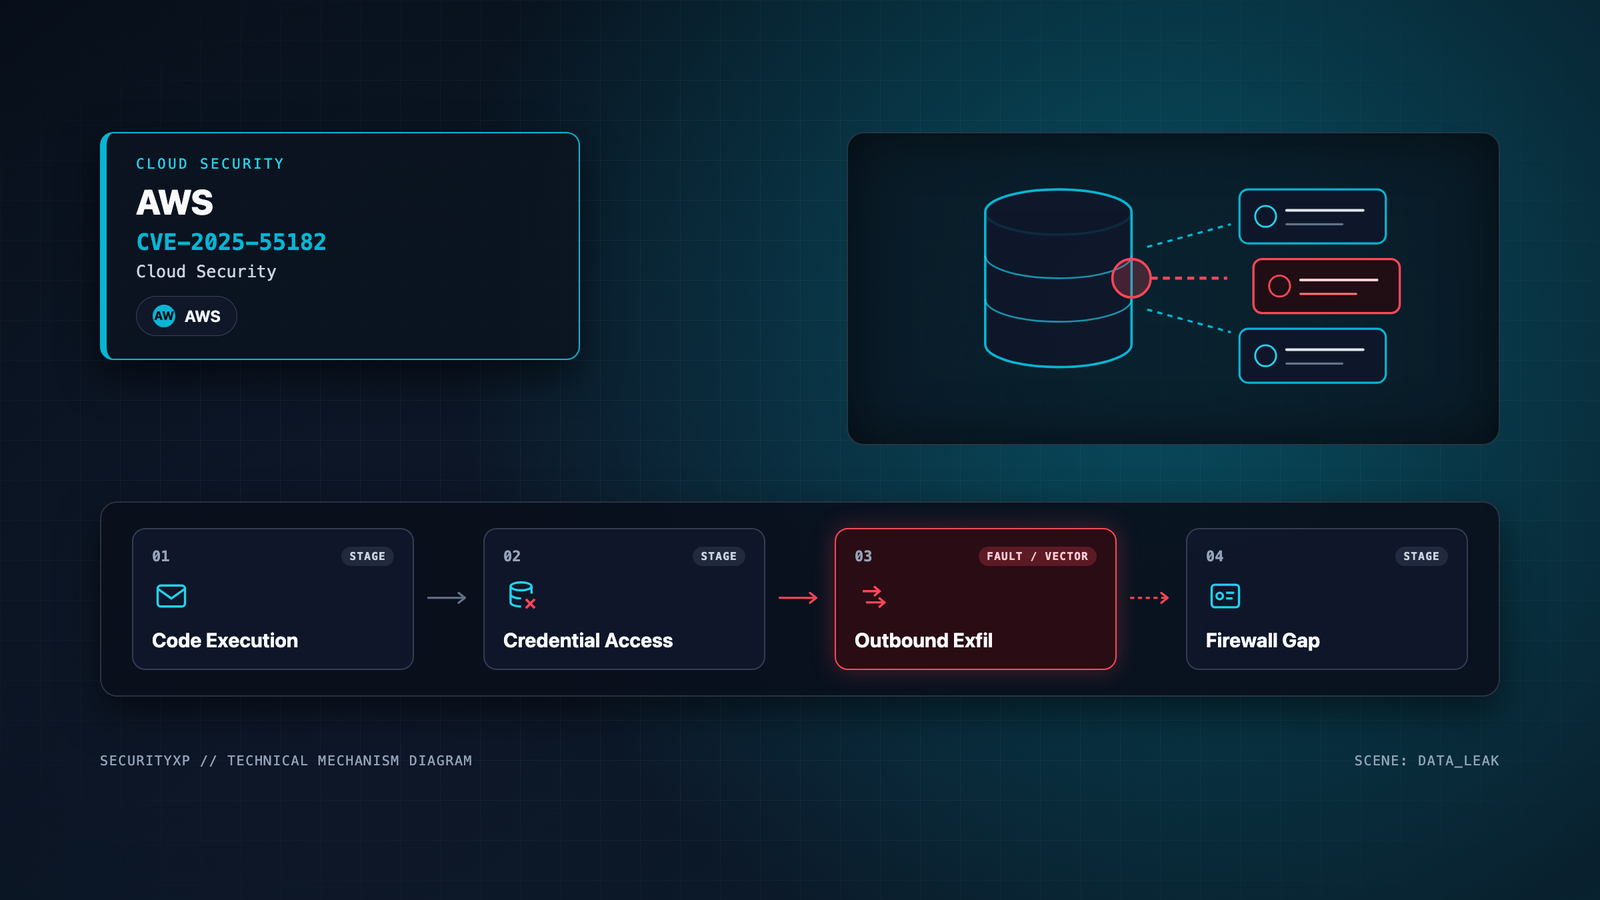
AWS Warns Outbound Traffic Blind Spots Can Enable Cloud Data Exfiltration
The AWS report shared with Cyber Security News (CSN) points to cases where unpatched vulnerabilities, such as CVE-2025-55182 (React2Shell), allowed attackers...
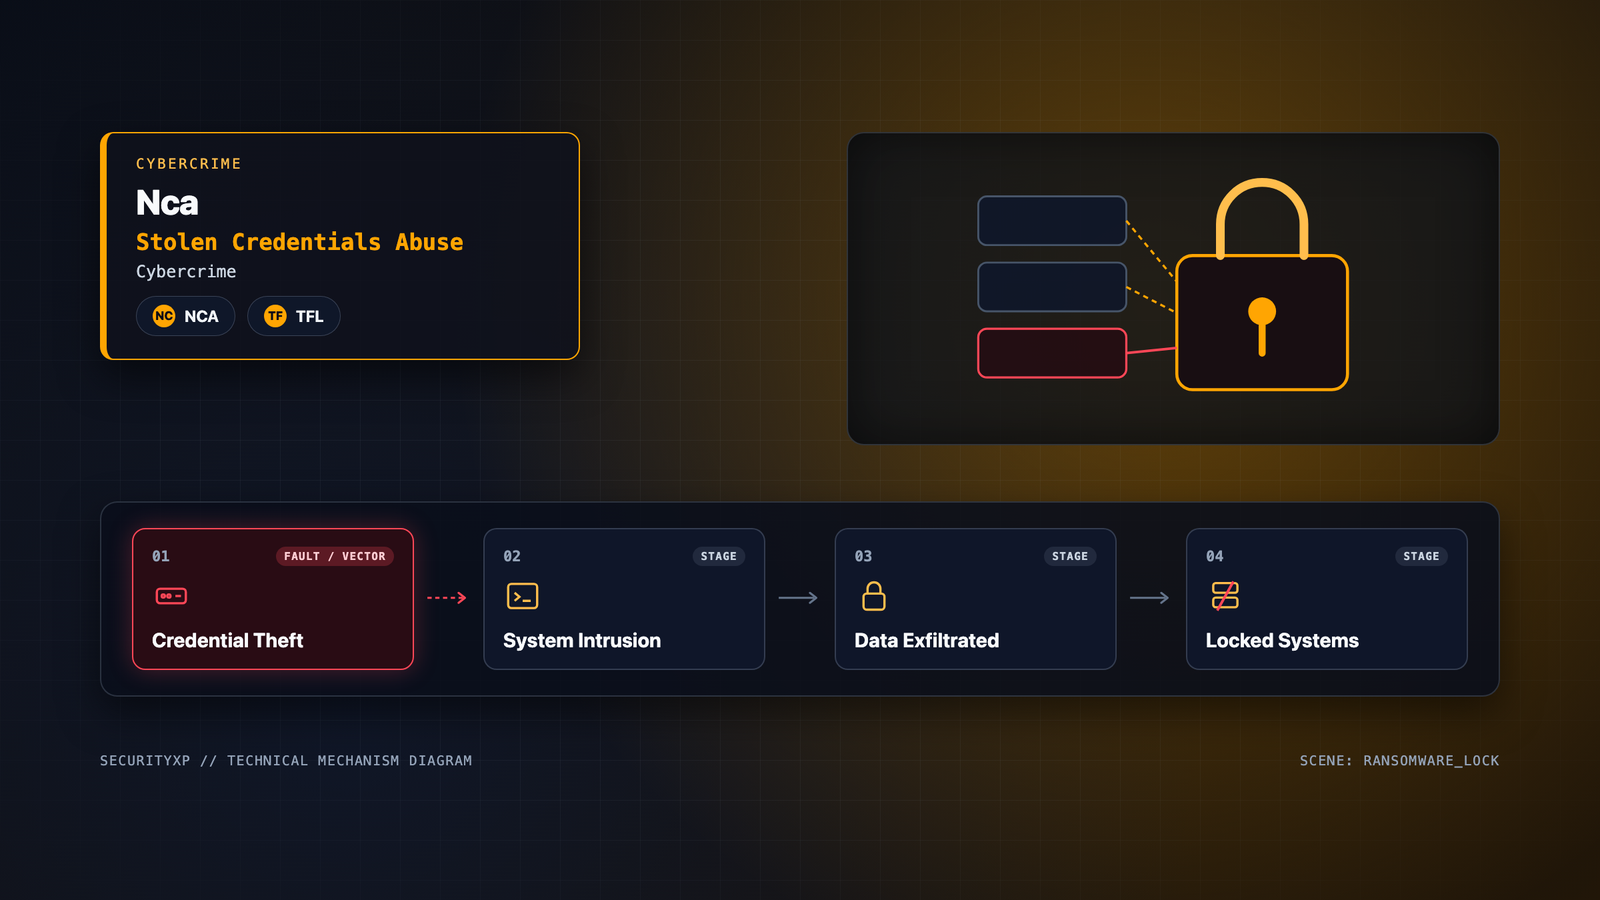
Scattered Spider Hackers Plead Guilty on Day 1 of Trial
According to the NCA, the cyberattack at TfL forced all 28,000 employees to visit their local offices to reset their passwords and caused £29 million...
On-Premises API Security on Kubernetes: What It Actually Looks Like in Practice
PCI DSS 4.0.1 now requires continuous API security testing and maintained API inventories. (These PCI DSS 4.0.1 requirements became mandatory on March 31...
Sunil Varkey Joins Hexaware Technologies as EVP & CISO
His responsibilities align with Hexaware Technologies’ broader technology and growth objectives as the company continues to support large-scale digital...

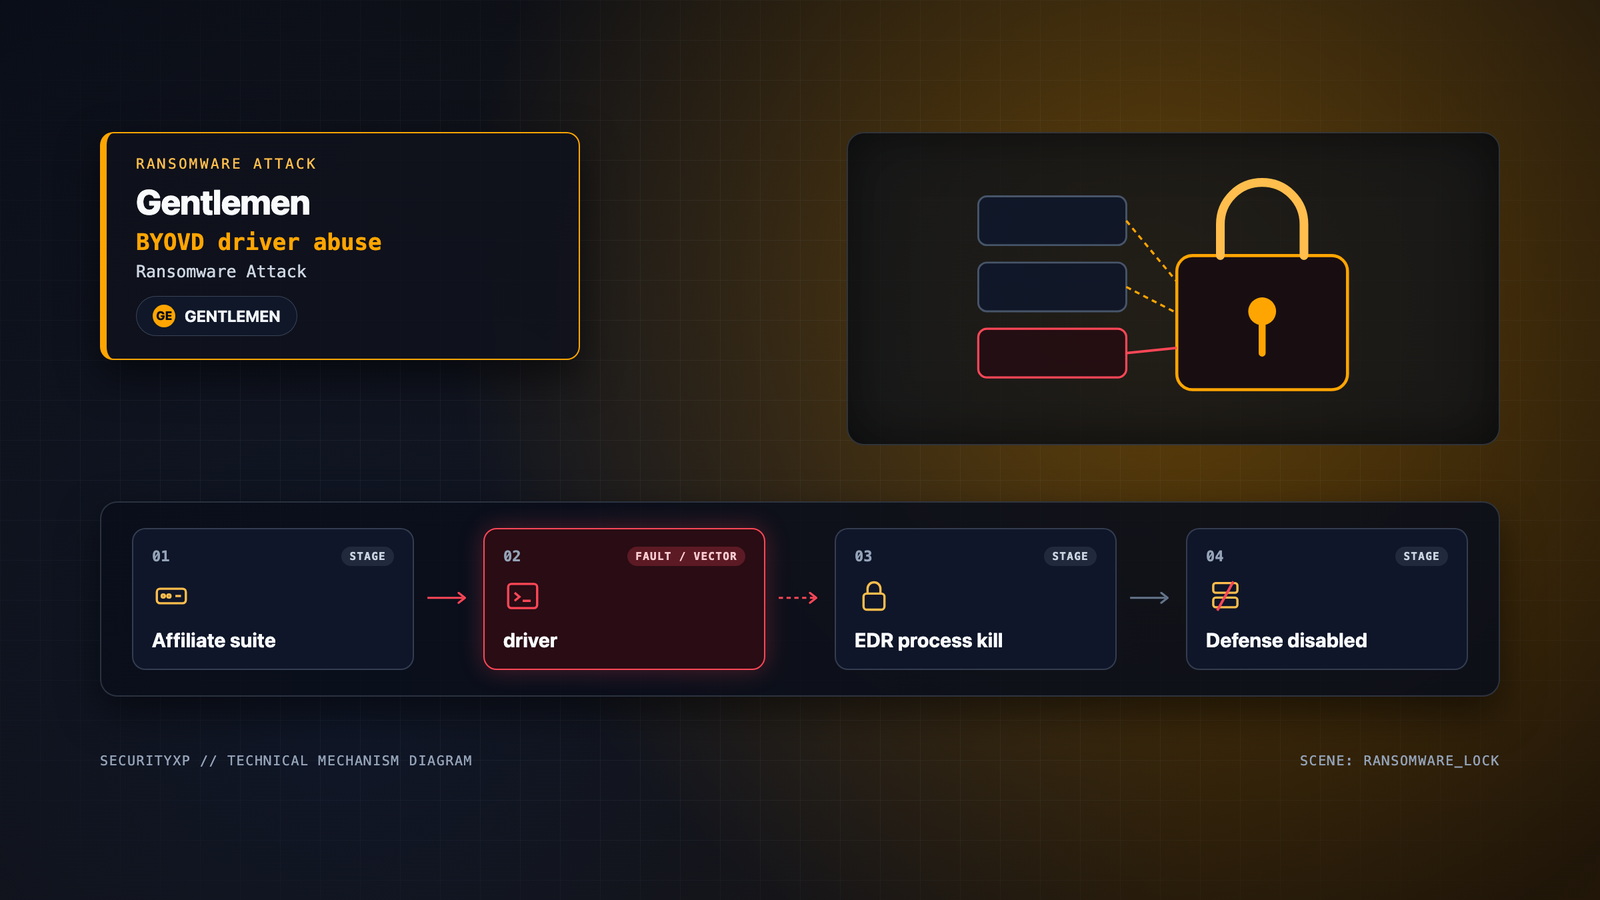
GentleKiller Ransomware Abuses Vulnerable Drivers to Disable 400+ EDR Security Processes
ESET says the Gentlemen RaaS gang's GentleKiller framework uses eight vulnerable drivers to kill more than 400 processes from 48 security products. Here is how it works and what to block.
Nancy Guthrie Case Reframed by Crypto Firm's "Wrench Attack" Label as Police Confirm Motive Pending
In it, CertiK described Nancy Guthrie's kidnapping as part of a "$6 million bitcoin ransom demand" and tied it to what the company called "the documented...

Virus vs Worm: Why the Propagation Difference Actually Matters
But no detection tool replaces patching: the vulnerability that WannaCry used had a patch available for eight weeks before the attack. In 1988, the Morris...
Week in review: 74k Fortinet firewall credentials stolen, Splunk Enterprise RCE under active attack
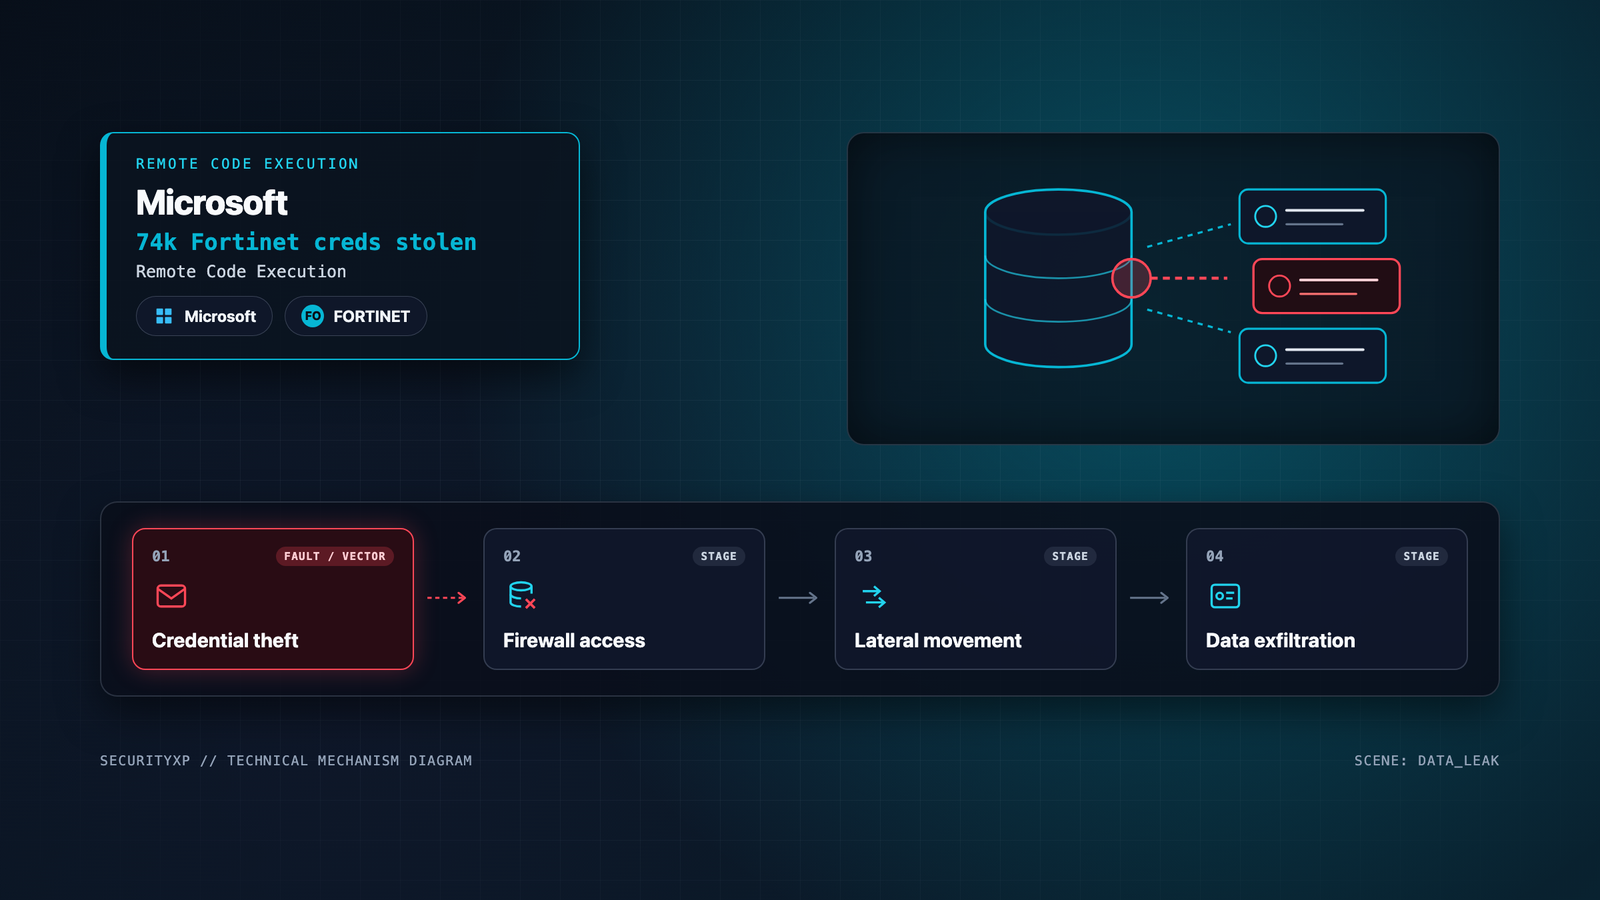
Microsoft working on patch for RoguePlanet Defender zero-day (CVE-2026-50656) Microsoft has acknowledged the local elevation of privilege issue in Microsoft...
Navigating the GPS Threat Landscape, with Brandon Karpf
If this research is accurate, these attacks represent a significant evolution for how defenders think about this critical technology. Key sources: -...
Privacy-Preserving Outsourced Witness Updates for Append-Only RSA Accumulators
In this paper, we present a privacy-preserving outsourced witness-update protocol for append-only RSA accumulators. The protocol combines witness updates...
Vulnerability response: Built for humans, outpaced by machines.
Frontier models now discover and chain vulnerabilities faster than human analysts can confirm them, and the gap between finding and fixing is shrinking in...