Author
SecurityXP
115 articles published RSS feed

SecurityXP delivers cybersecurity news, vulnerability analysis, data breach reports, and threat intelligence.
Articles
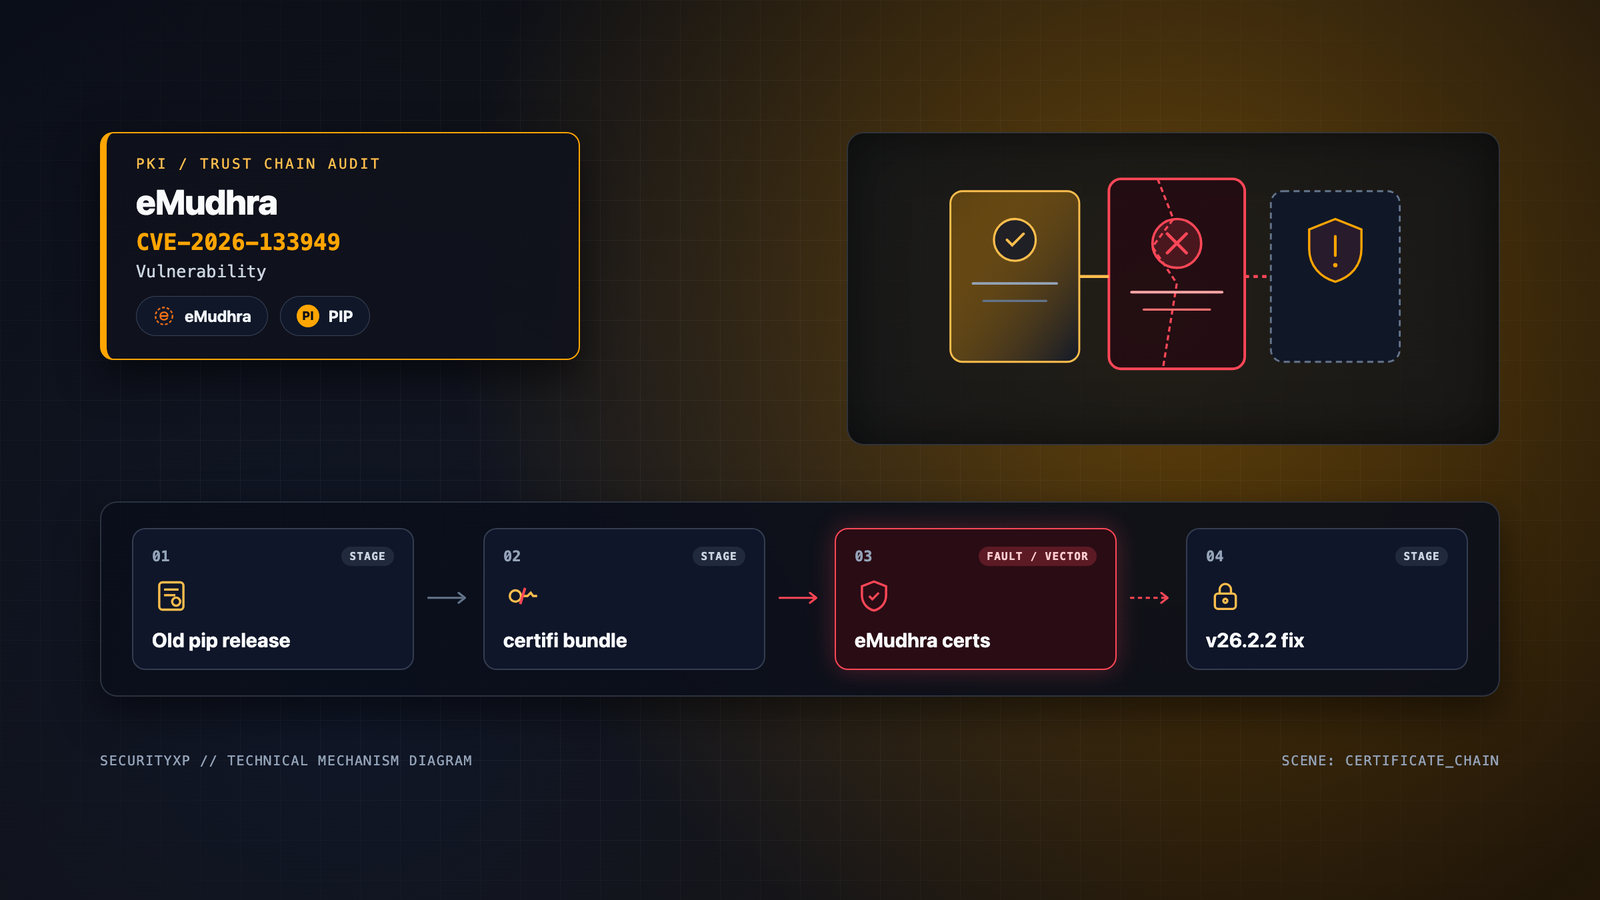
115 totalpip Before v26.2.2 Bundles Compromised eMudhra Certificates in certifi (CVE-2026-133949, CVSS 9.3)
pip releases earlier than v26.2.2 ship a certifi bundle that contains the compromised eMudhra certificates.
Ransomware Recovery Stretches to a Median of 20 Days as Attackers Push Into the Backup Layer
Organizations hit by ransomware need a median of 20 days to achieve full restoration, and 28% take more than six weeks to return to normal, according to Rubrik's 2026 report.
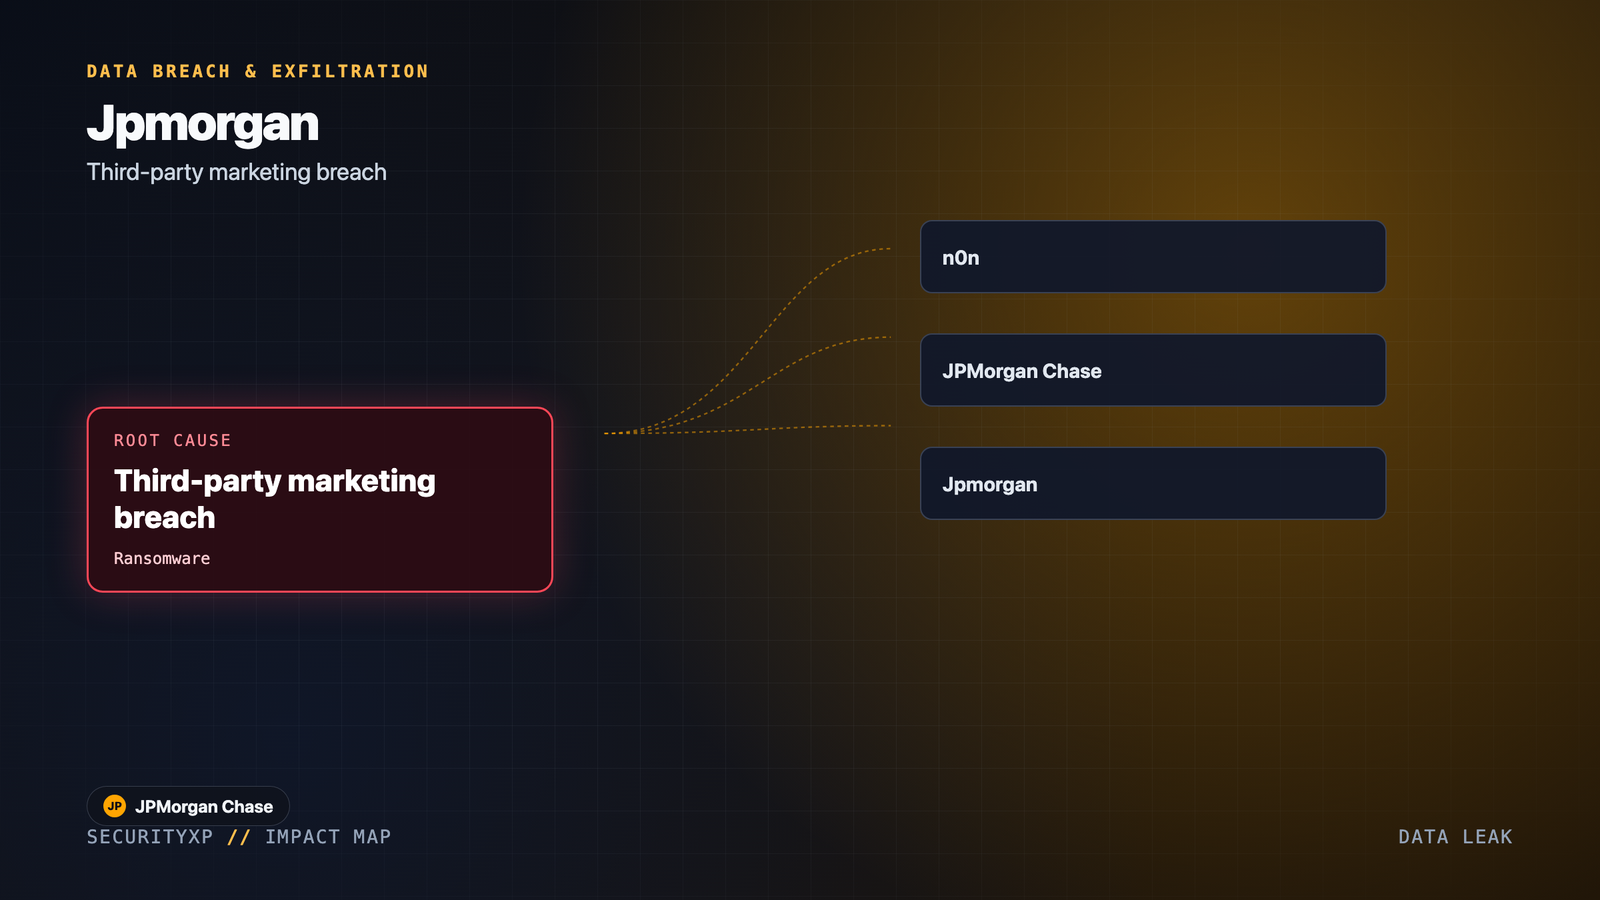
n0n Publishes 16,000 JPMorgan Reserve Card Emails After Vendor Breach
Roughly 16,000 customer email addresses have been published in a dataset apparently linked to JPMorgan Chase's invitation-only Reserve card program…
Chinese-Nexus Hackers Used an Exposed Cairn AI Instance to Find and Exploit an Apparent Zero-Day
Amazon Threat Intelligence says Chinese-nexus hackers used Cairn, an open-source autonomous AI penetration-testing framework, to discover an apparent…
FBI Criminal Database Breached Again, Second Hack in Months Targets US Crime Records
The FBI's criminal database has been hacked for the second time in months, according to reports from India Today and Hindustan Times.
SonicWall Ends Gen 6 Firewall Patching, Even for Critical Flaws
Google Mandiant’s M-Trends report, published in March 2026, estimated the mean time to exploit vulnerabilities at -7 days, meaning exploitation on average…
Cisco Expressway Flaw Exploited Shortly After PoC Release to Breach Russian Organization
Attackers used CVE-2026-76466, a CVSS 9.8 Cisco Expressway flaw, to breach a Russian organization soon after a public PoC, F6 reports.
VMware vCenter Authentication Bypass Exploited as Zero-Day for Over Two Months Before Patch
Broadcom's VMSA-2026-0009 fixes CVE-2026-123890, a vCenter authentication bypass exploited as a zero-day. Affected versions, fixed builds and hunting guidance.
Trojanized Claude Code Builds Sat in Cursor's Marketplace for 11 Hours
Attackers distributed malicious versions of Anthropic's Claude Code extension through Cursor's extension marketplace.
Auditing the State Transfers That Execution Traces Miss in Long-Horizon LLM Agents
A paper submitted on 17 Nov 2026 to Computer Science Cryptography and Security, “Securing and Auditing Long-Horizon LLM Agents: State-Transfer Auditing…
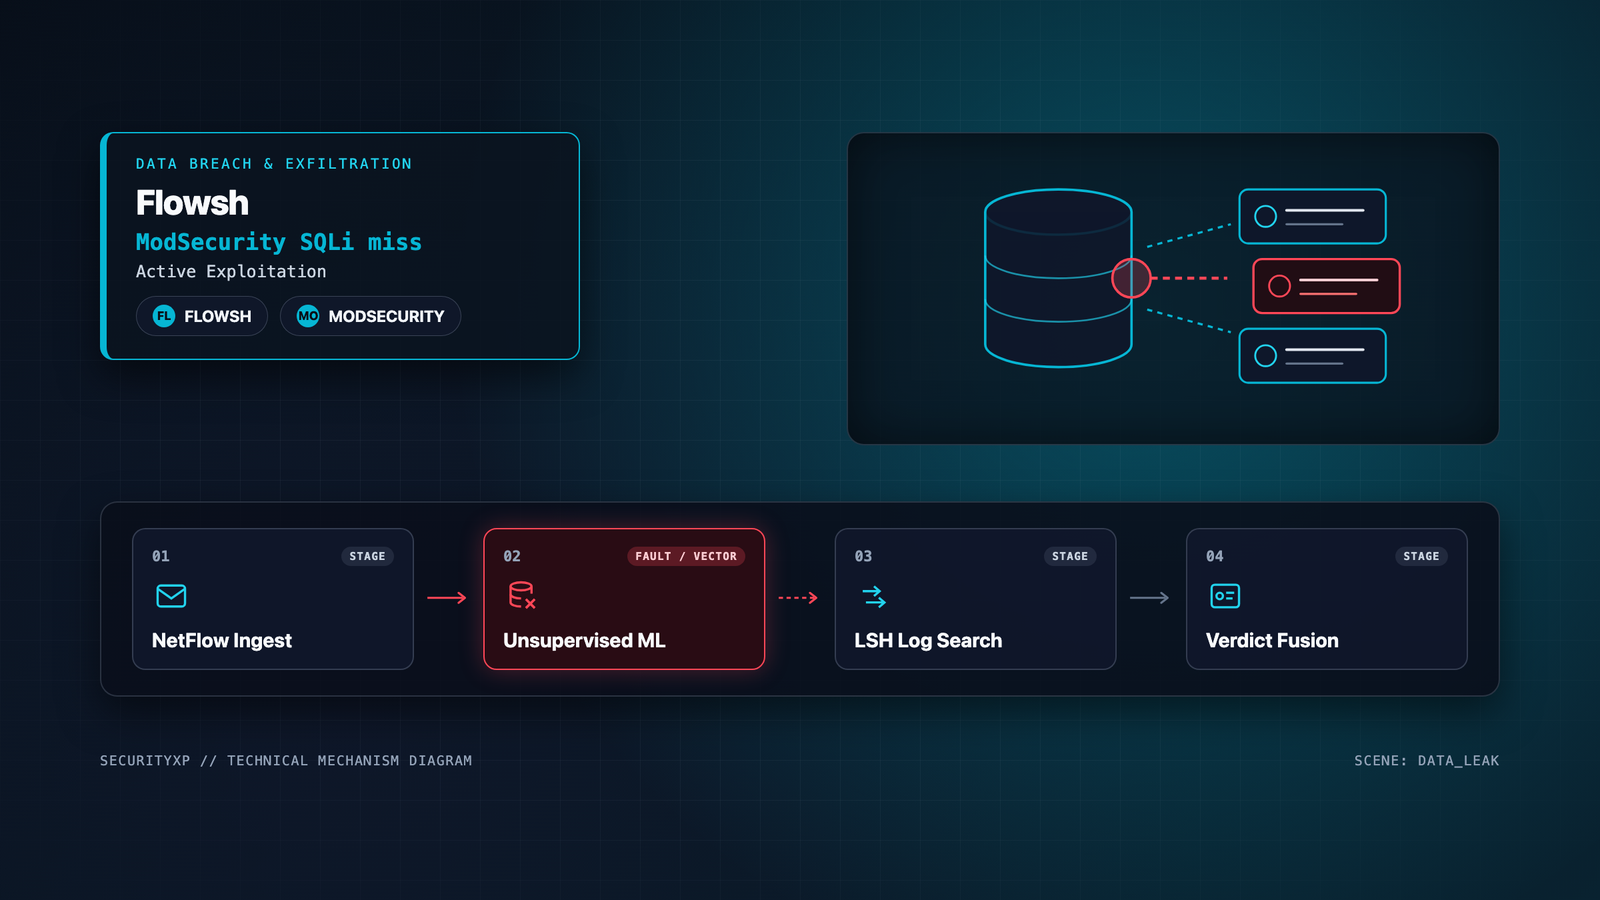
FlowSH Correlates Anomalous NetFlows With Server-Side Logs to Catch SQLi That ModSecurity Misses
FlowSH, a detection system posted 18 November 2026 under Computer Science Cryptography and Security, combines unsupervised machine learning on network…
Nvidia Investigating Gentlemen Ransomware Group's Claim of Stolen Data
Nvidia is investigating an incident that may have affected a third-party partner after the Gentlemen ransomware group added the chipmaker to its dark web…
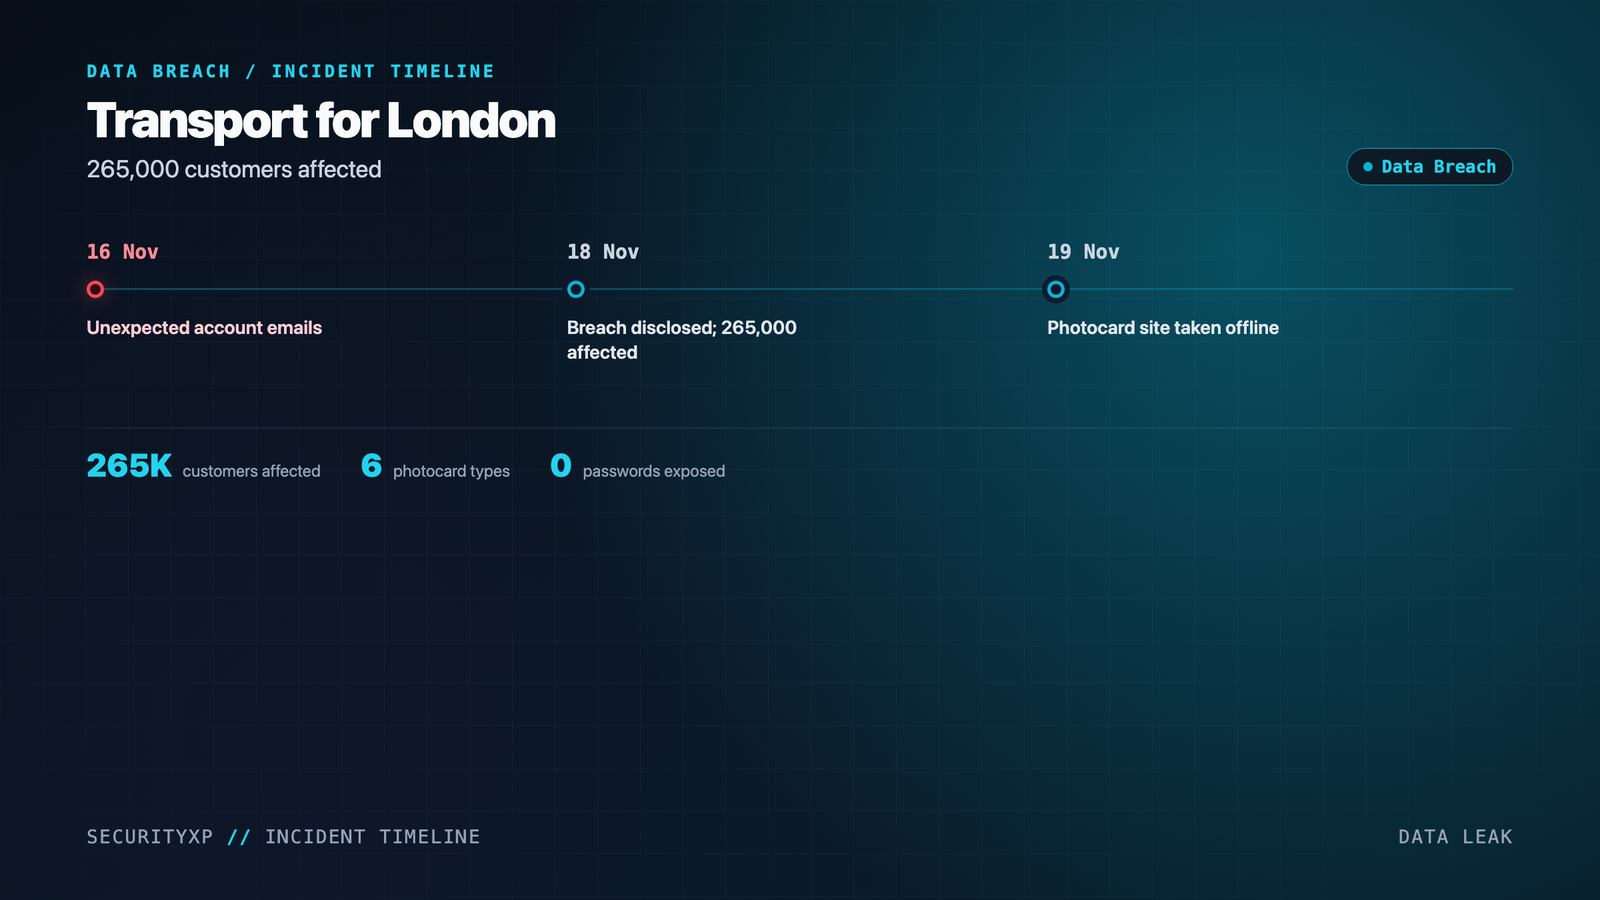
TfL Pulls Oyster Photocard Site Offline After Breach Compromises About 265,000 Accounts
Transport for London has shut down its Oyster photocard website after attackers compromised customer accounts, in an incident TfL says may have affected…
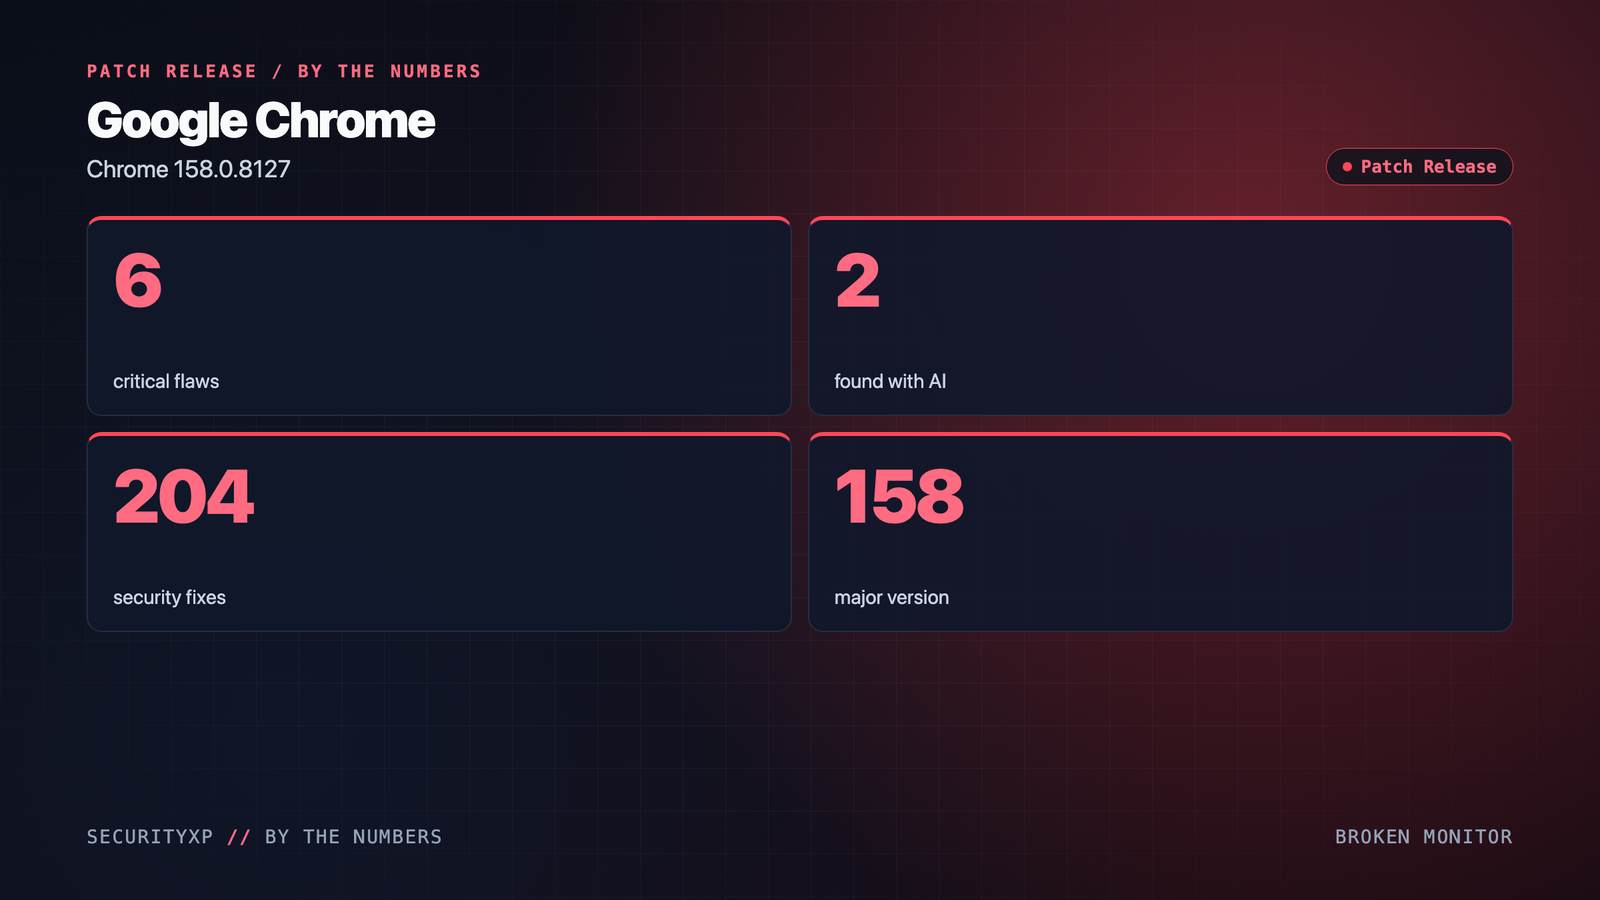
Chrome 158 Ships Two Critical Memory-Safety Fixes, Both Credited to AI-Assisted Research
Google has published a Stable channel update for Chrome on Windows, Mac and Linux.
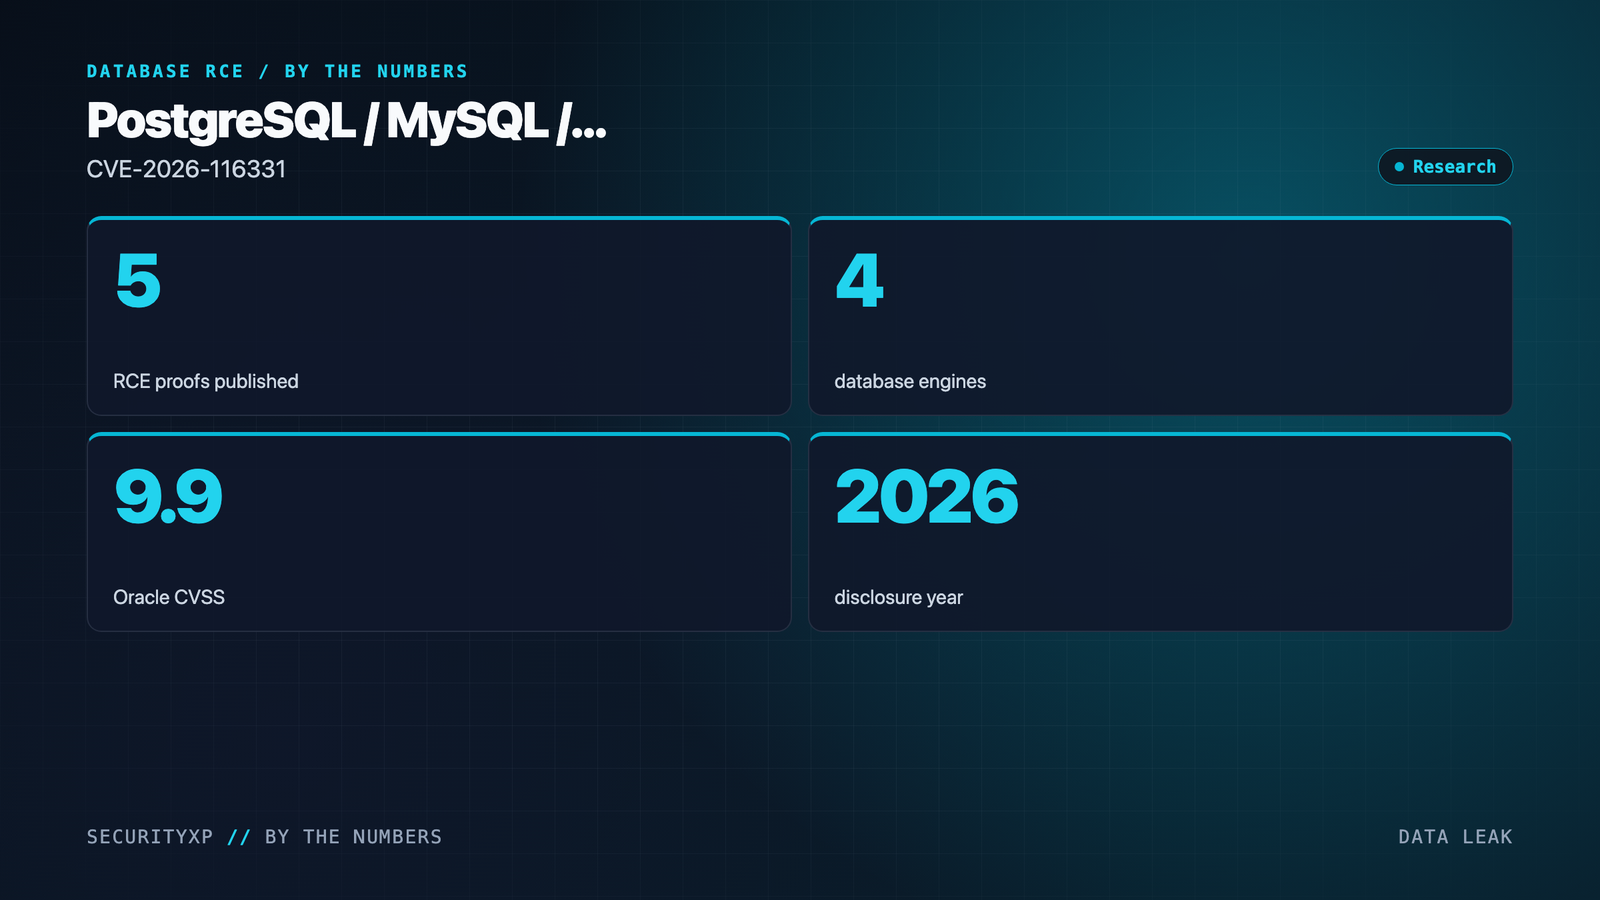
Researcher Publishes Code-Execution Proofs for PostgreSQL, MySQL, Oracle and ClickHouse
A researcher has published proof-of-concept exploits for five code-execution flaws in PostgreSQL, MySQL, Oracle and ClickHouse.
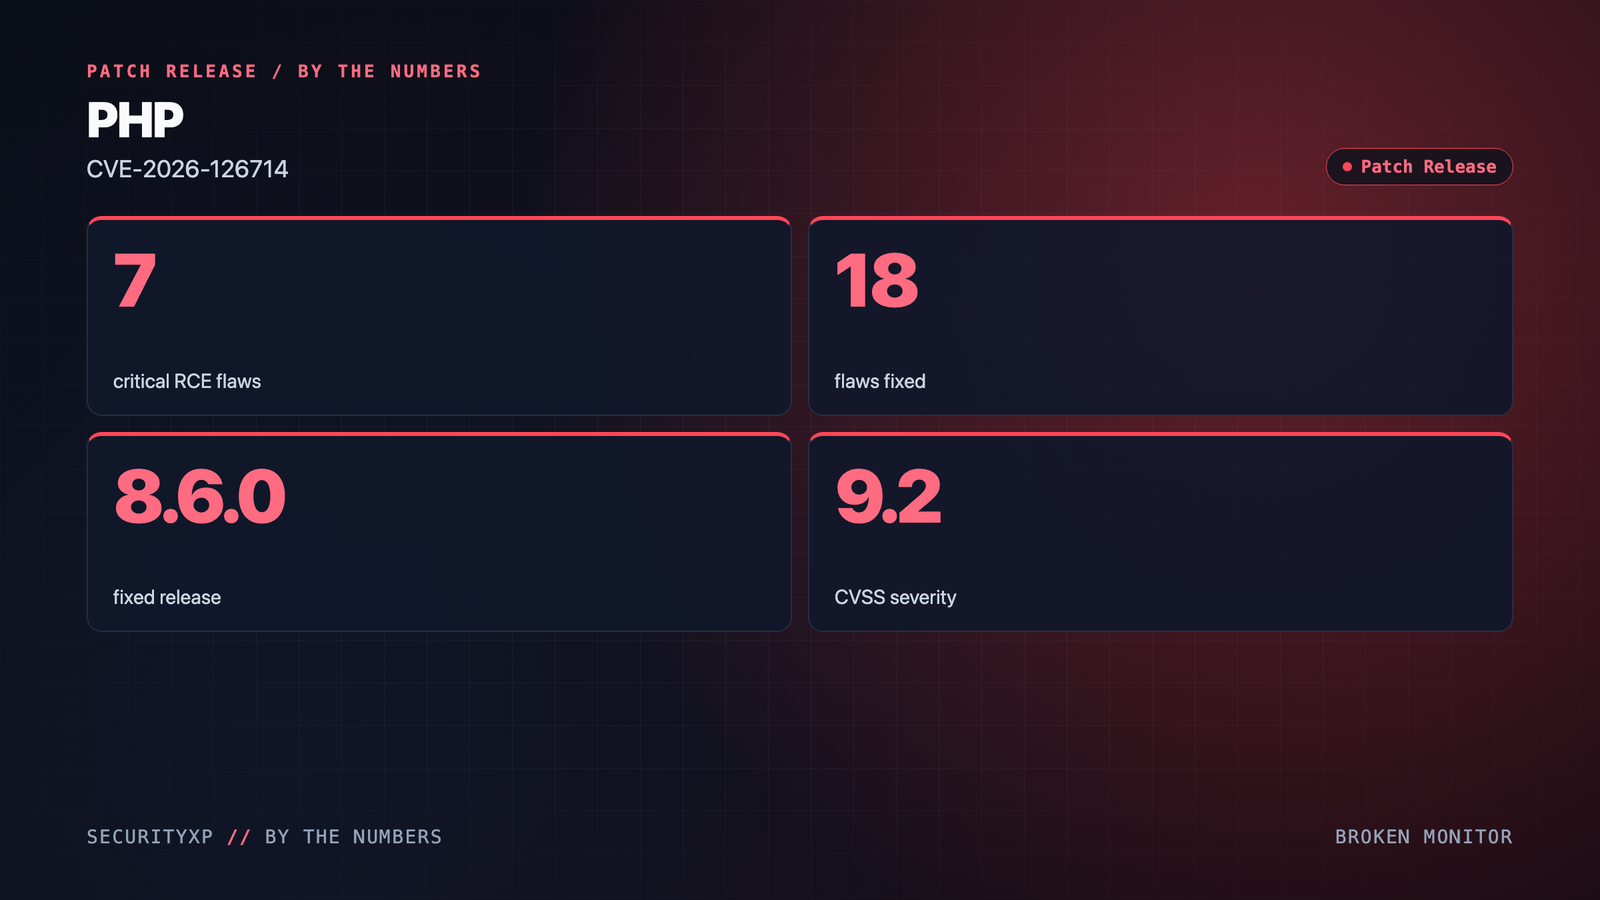
PHP 8.6.0 Carries the Fix for CVE-2026-126714, the 9.2-Rated Flaw October's Releases Left Open
PHP 8.6.0, released today, includes the fix for CVE-2026-126714, a flaw that PHP's maintainers rate 9.2 out of 10 on the CVSS 4.0 scale.
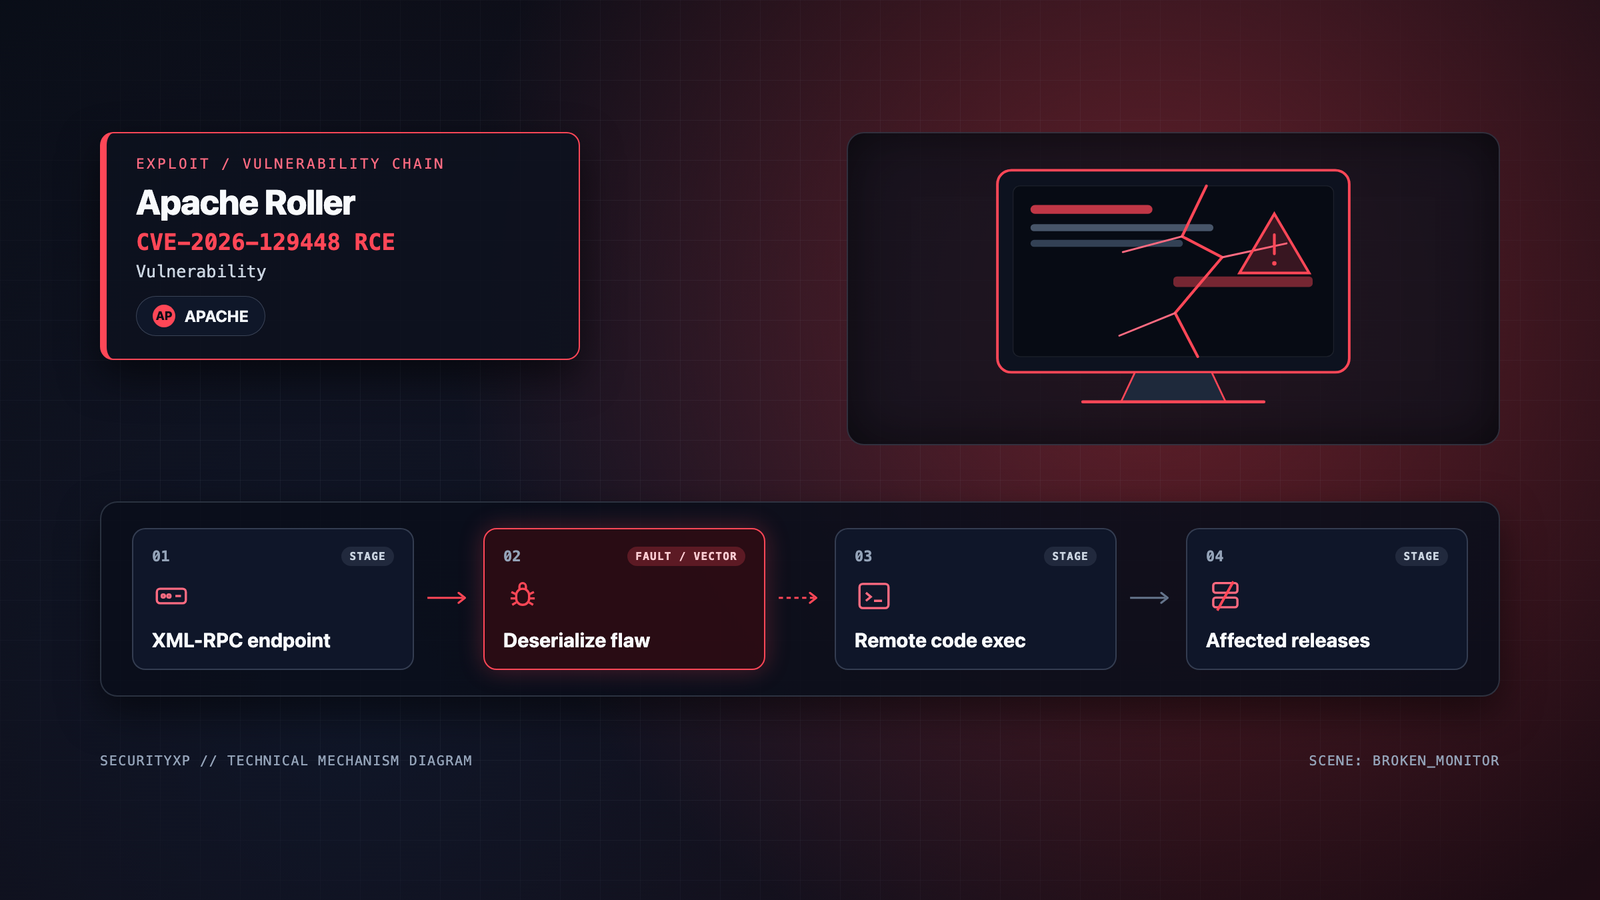
Apache Roller Widens Actively Exploited RCE Flaw to Versions 4.0.0–6.1.4
Apache Roller is an open-source, Java-based blogging platform.
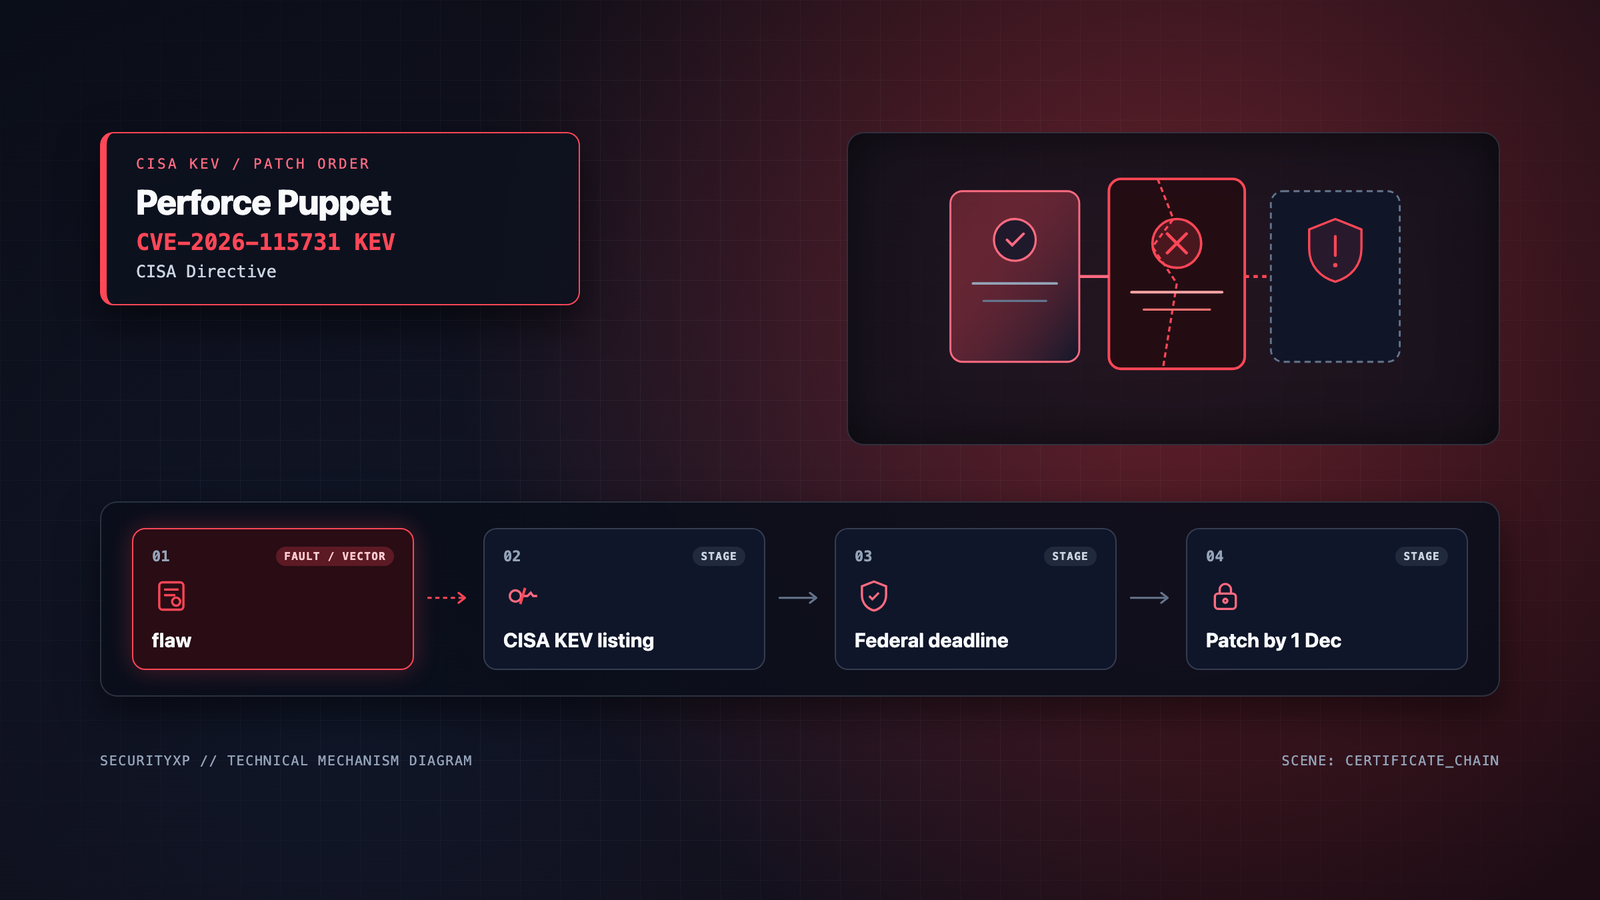
CISA Orders Federal Agencies to Patch Exploited Puppet Enterprise RCE by December 1
On Tuesday, the US Cybersecurity and Infrastructure Security Agency added CVE-2026-115731 to its Known Exploited Vulnerabilities catalog.
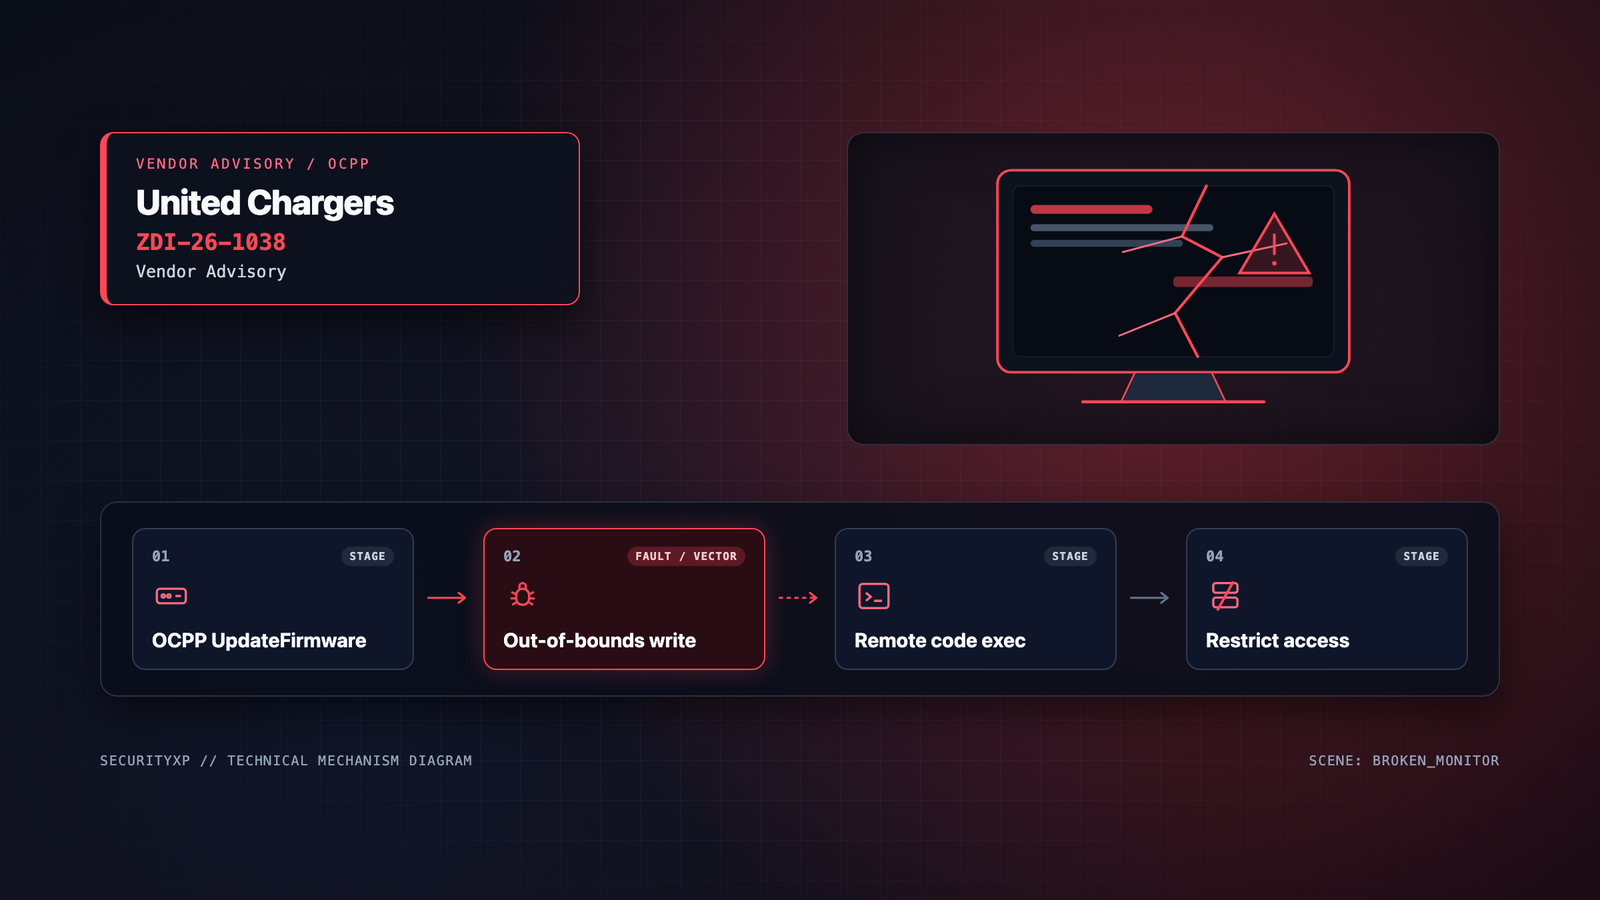
Grizzl-E Smart 40A Charger Flaw Lets a Nearby, Unauthenticated Attacker Run Code
The Zero Day Initiative's advisory on the United Chargers Grizzl-E Smart 40A EV charger is short, and one sentence carries the weight: the vulnerability…
NGINX2Root: Five Critical NGINX RCE Flaws and the Limits of the Public Exploit Record
On November 18, F5 released an out-of-band security update covering 10 vulnerabilities in NGINX Plus and NGINX Open Source.