Author
SecurityXP
115 articles published · Page 4 of 6 RSS feed

SecurityXP delivers cybersecurity news, vulnerability analysis, data breach reports, and threat intelligence.
Articles
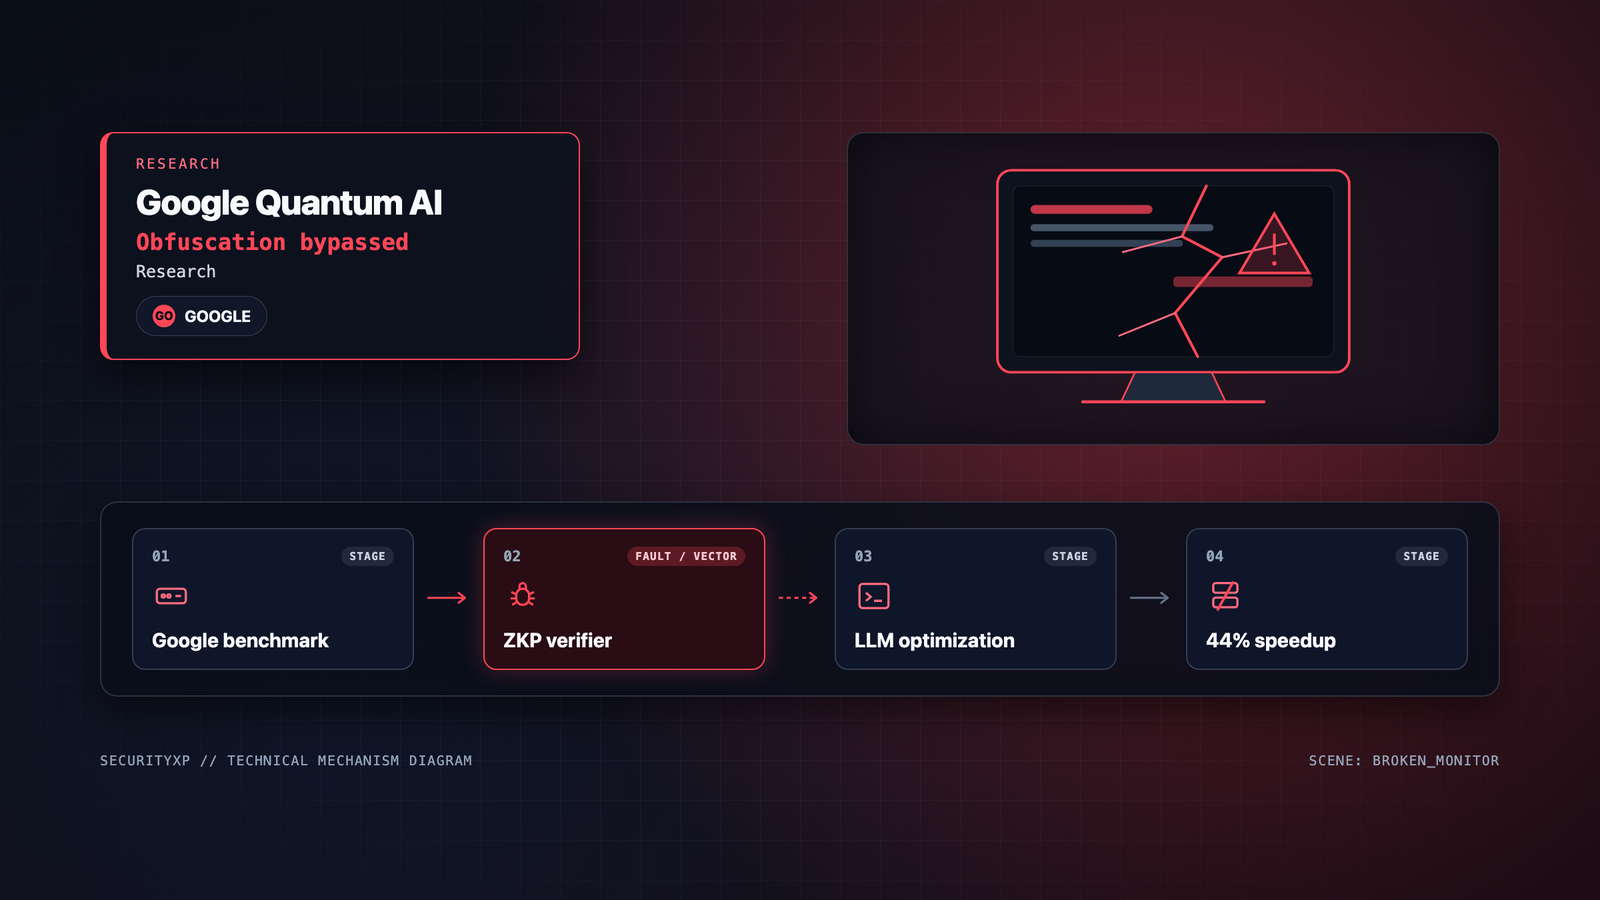
115 totalGoogle Shor's Algorithm Obfuscation Broken: LLM Crowdsourcing Outperforms ZKP-Verified Benchmark by 44%
An open-source contest utilizing Large Language Models (LLMs) has successfully reverse-engineered and optimized Google Quantum AI's restricted Shor's algorithm circuit optimization, exceeding Google's obfuscated benchmark by 44.0%.
Form: Report a suspected breach of farming rules or fraud
Report a suspected breach of farming rules or fraud How to report a suspected breach of farming rules or fraud to the Rural Payments Agency. Applies to...
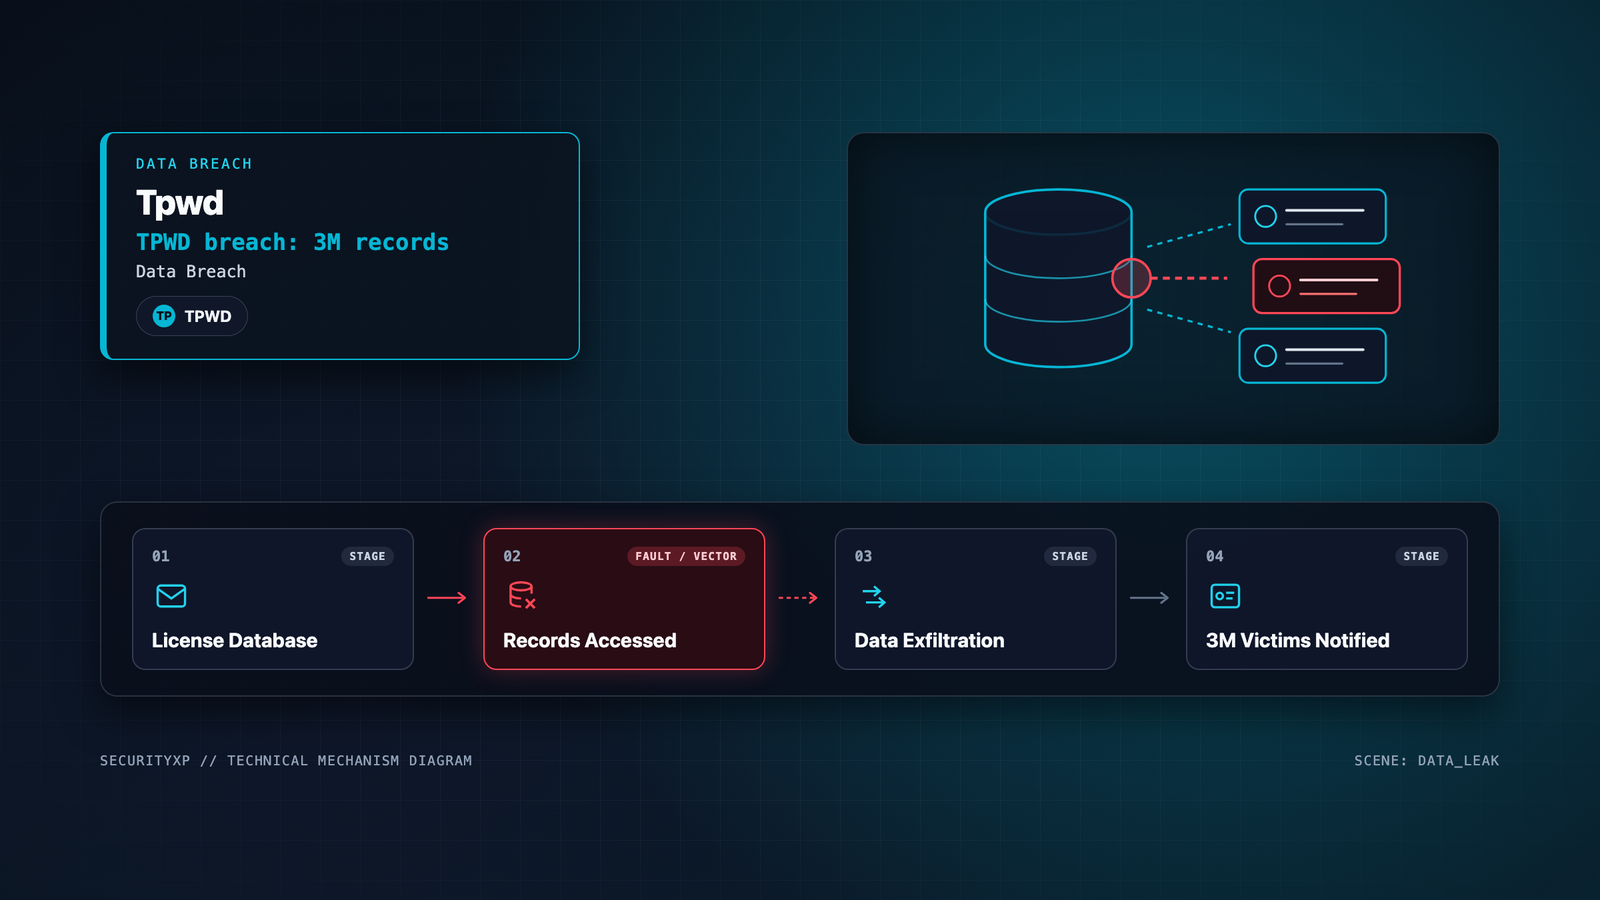
Major Data Breach Warning Issued for 3 Million in Texas: What To Know
Major Data Breach Warning Issued for 3 Million in Texas: What To Know...
Hackers Exploit Gravity SMTP WordPress Plugin Bug to Expose API Keys Vulnerability (CVE-2026-4020)
The vulnerability, tracked as CVE-2026-4020 (CVSS score: 5.3), is a medium-severity information disclosure flaw that can allow unauthenticated attackers to...
Klue OAuth breach victim list grows as Icarus hackers claim attack
Market intelligence platform Klue has publicly confirmed a recent security incident that allowed threat actors to steal OAuth tokens used to connect to...
Spur adds no-code Cloudflare integration for Monocle
"These updates ensure that customers can implement inline enforcement in minutes, gain deeper visibility into user behavior, and quickly translate those...
The Gentlemen RaaS Uses GentleKiller EDR Framework Targeting 400 Security Processes
It allows The Gentlemen operators to integrate abused drivers into their toolset very soon after an EDR killer PoC is disclosed." The third-party...
AI-Enabled Hacker Caught: Leaked Prompts Expose Resume and IP Address
A fully AI-enabled hacker was caught, revealing his full system prompts, which included his resume and his IP address.
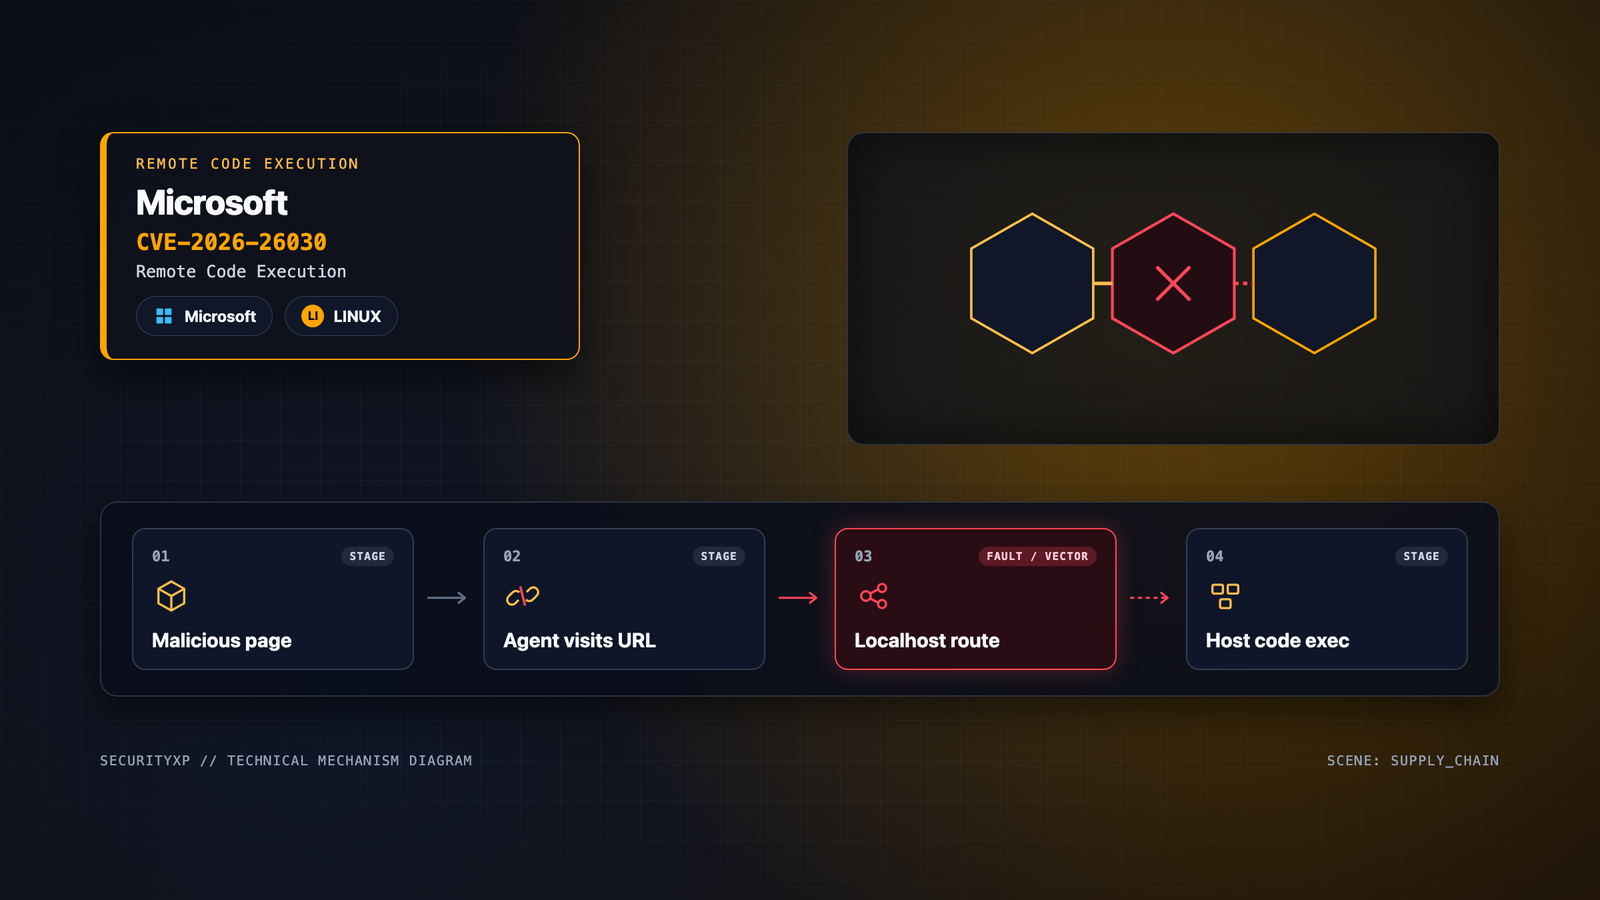
AutoJack Attack Lets One Web Page Hijack AI Agent for Host Code Execution
Microsoft made a similar localhost argument in its Semantic Kernel RCE research, tracked as CVE-2026-26030 and CVE-2026-25592. The issue is tracked as...
Meteor 3.0 Migration Helped Rocket.Chat Move Off End-of-Life Node.js Runtime
Supply-Chain Risk Without a CVE Meteor 3.0 puts a name to a category of supply-chain risk that standard vulnerability management does not always catch. The...
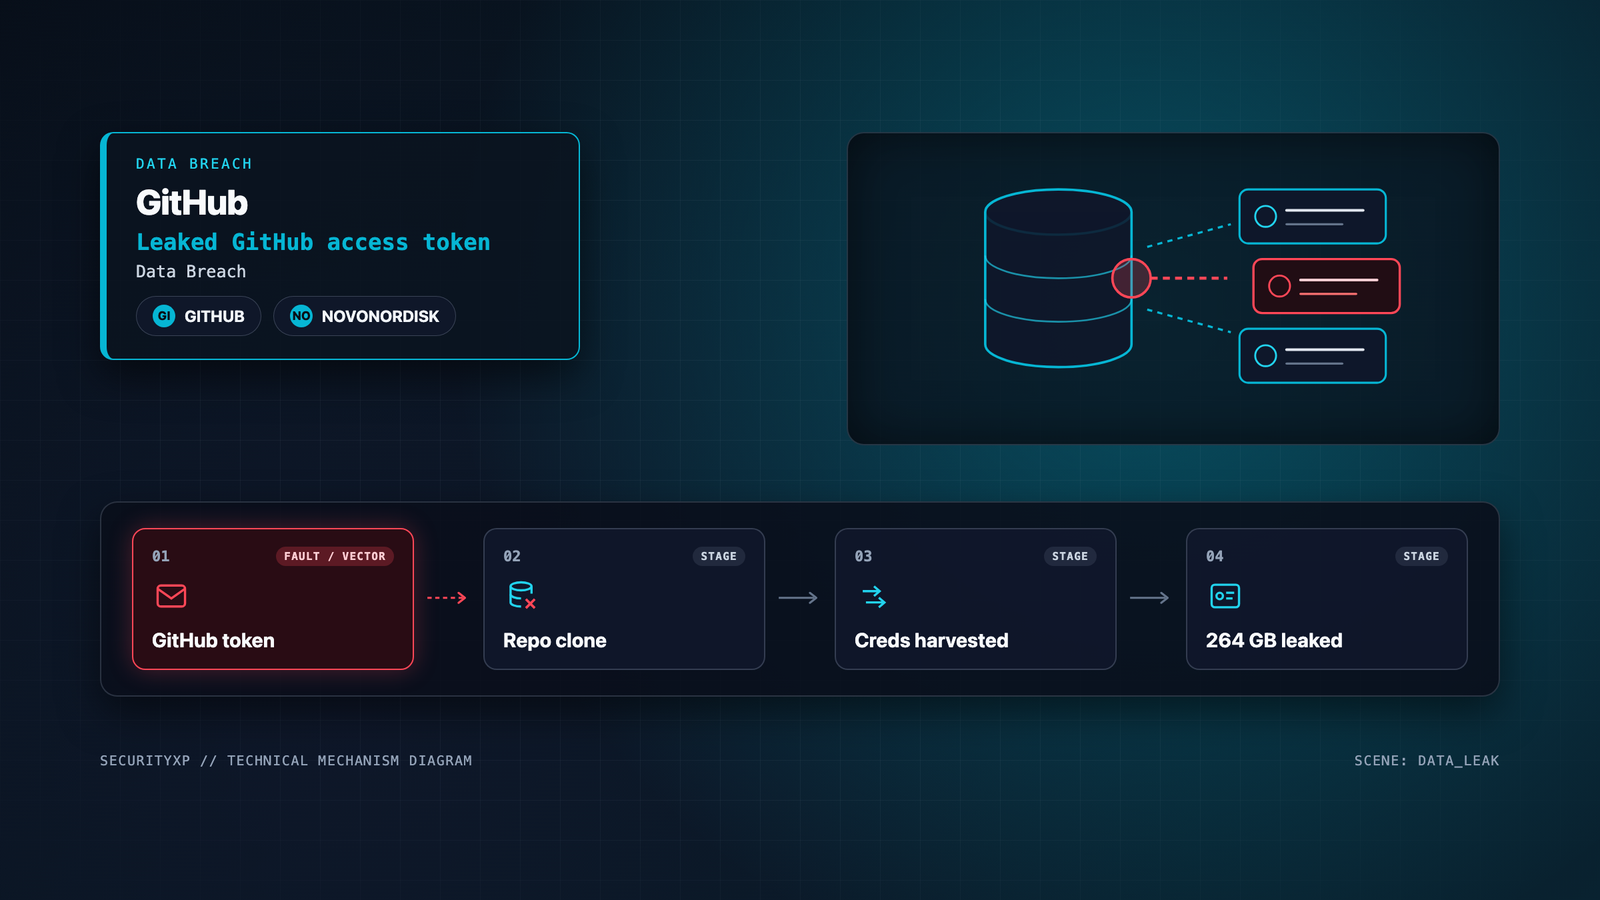
Novo Nordisk Breached: Ozempic Maker Suffers 264 GB Data Leak
They allegedly breached Novo in March via a GitHub access token that let it clone the company's repositories and find additional credentials.
Weekly Metasploit Update: NTLM Relay Priv Esc, MCP Server Integration, Paperclip AI RCE Chain, and more
New module content (5) Paperclip AI RCE using a chain of six API calls (CVE-2026-41679) Authors: Sagilayani https://github.com/sagilayani and h00die-gr3y...
14,971 WordPress Sites Cleaned in Global SocGholish Takedown
Data from Infoblox shows that approximately 55% of its cloud customers attempted to reach SocGholish infrastructure this year alone, with the attacks...

Apple Patches Beats Studio Buds Flaw That Could Turn Earbuds Into a Wiretap
The security update fixes CVE-2025-20701, a vulnerability discovered by Dennis Heinze and Frieder Steinmetz of German cybersecurity firm ERNW. The issue is...
Every AI Agent Is an Identity. Most Organizations Don't Treat Them That Way
This is no longer theoretical, 65% of organizations experienced a security incident involving an AI agent in the past year, with 61% reporting exposure or...
What Is Application Security Testing? Tools and Types
Organizations that already enforce quality gates in CI/CD can extend that model into deployment workflows by requiring review of critical cloud exposures...
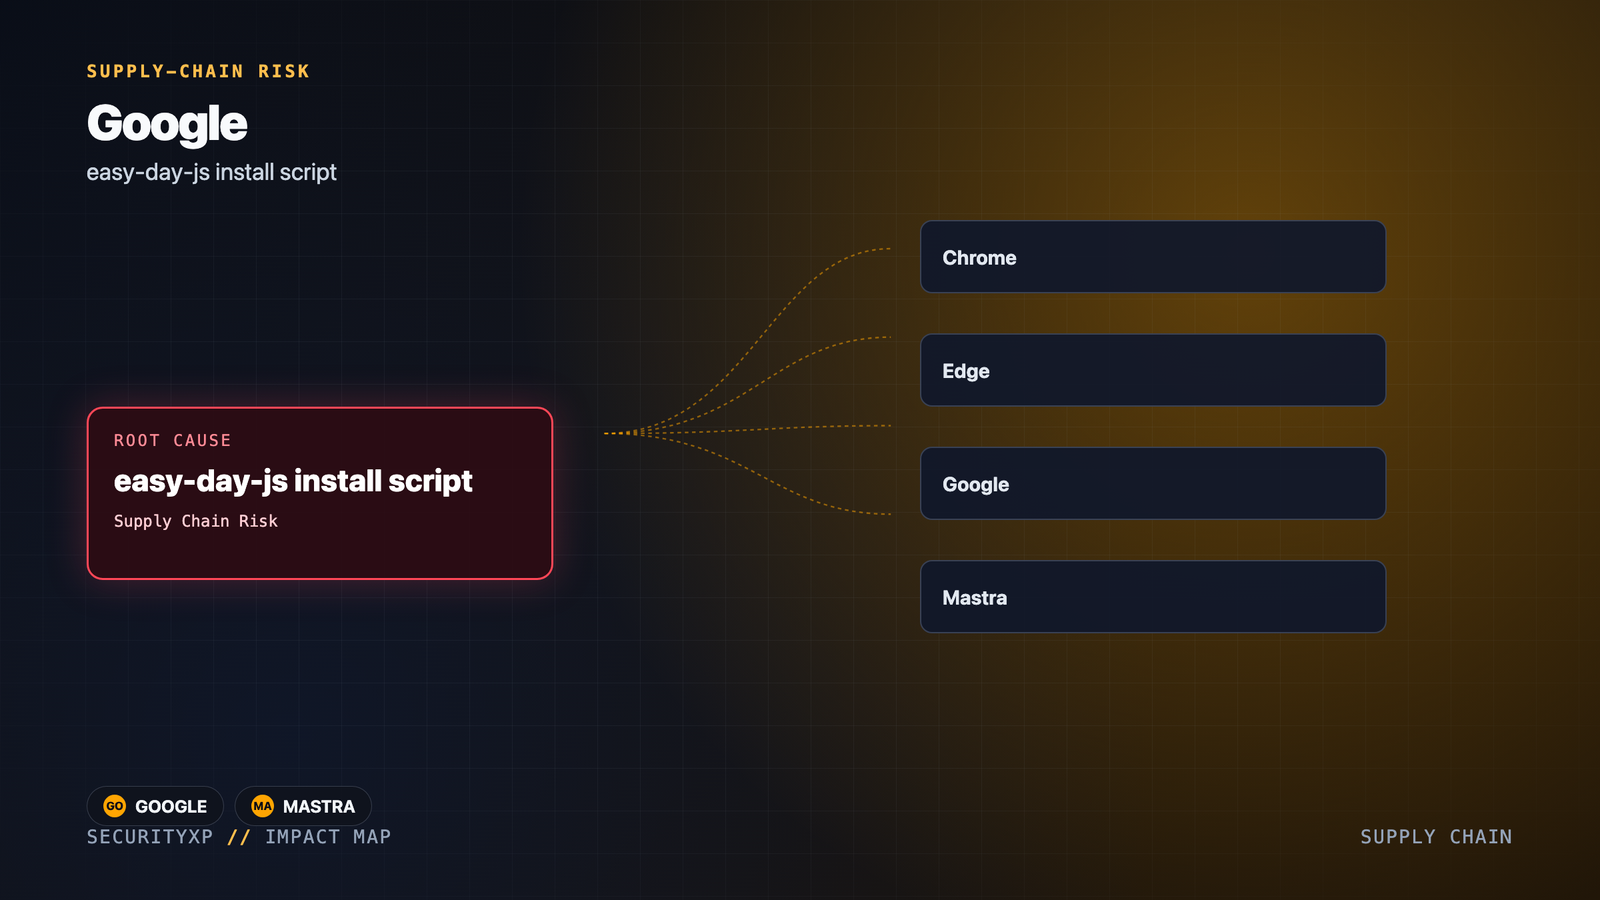
Mastra npm packages compromised in 'easy-day-js' supply chain attack
By exploiting npm’s install-time script execution, attackers gained the ability to harvest browser data from Chrome, Edge, and Brave, extract credentials...
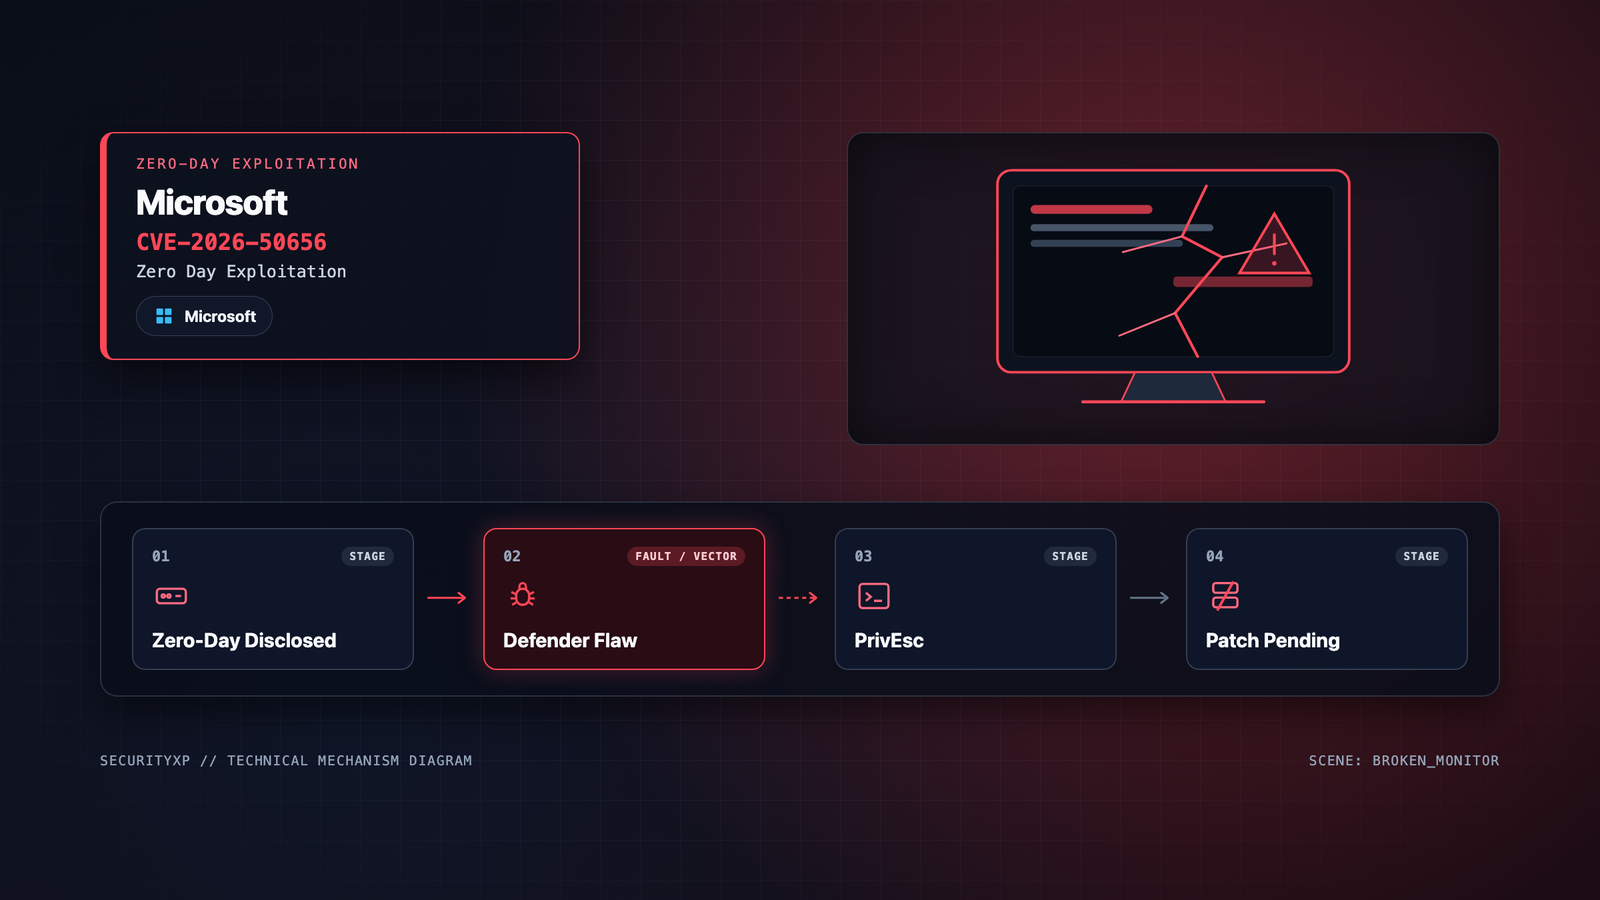
Microsoft Confirms RoguePlanet Zero-Day in Defender, Patch Under Development
I think it even works in the case of passive mode, but not really sure, haven't tested that." Microsoft told The Hacker News last week that it's aware of the...
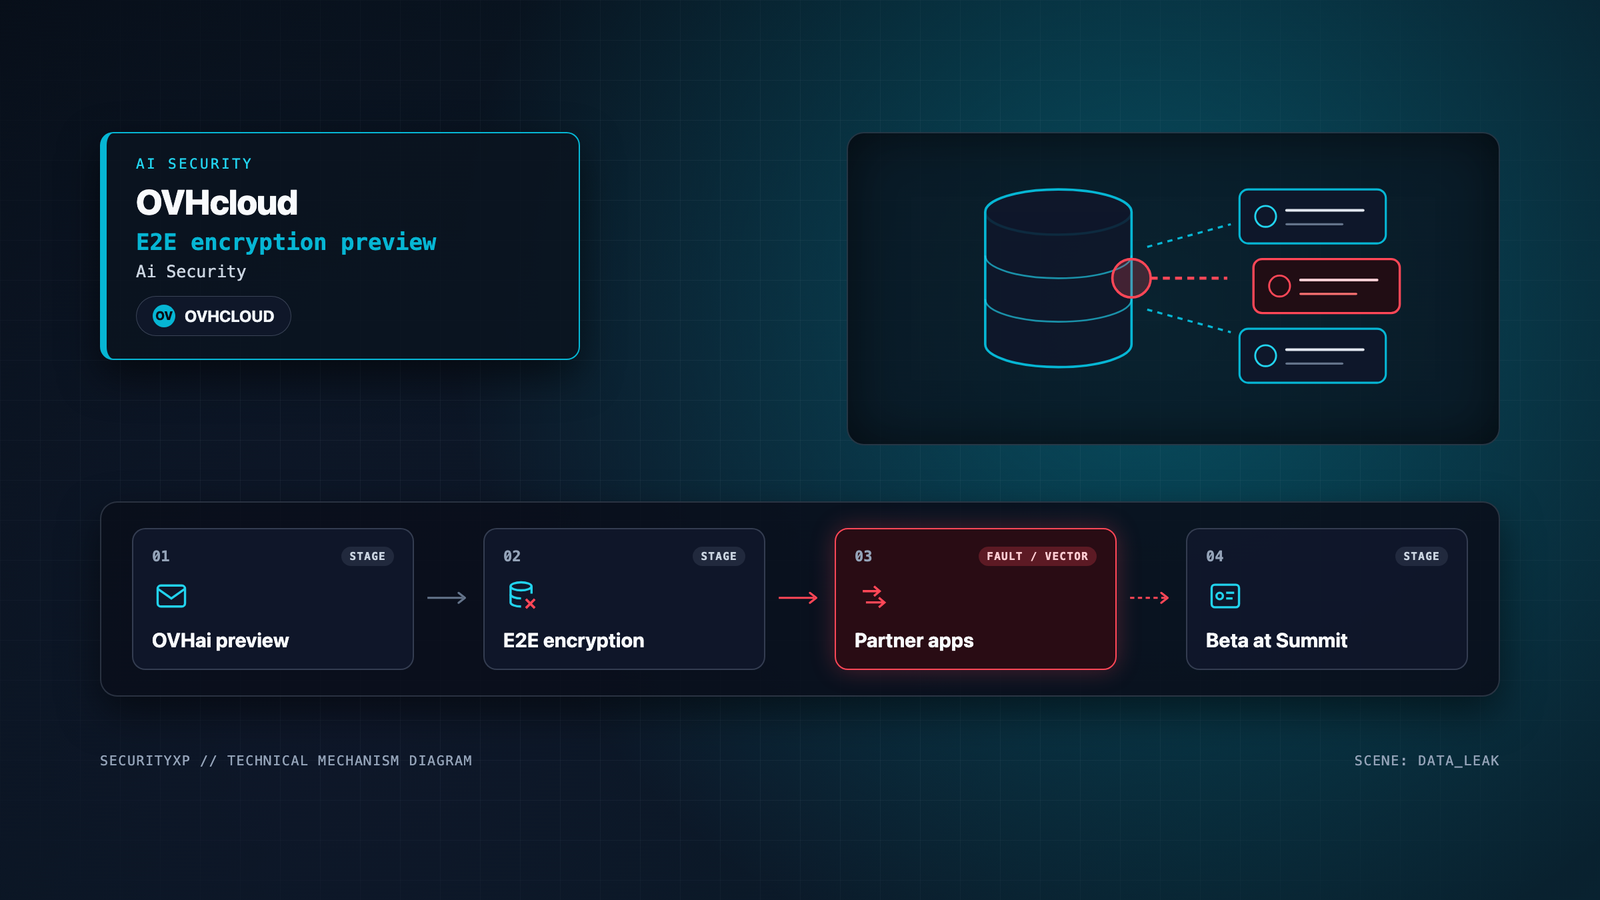
OVHcloud previews AI workspace with encrypted tools
OVHcloud says OVHai Workspace includes an end-to-end encryption option covering data and communications, including within partner applications integrated...
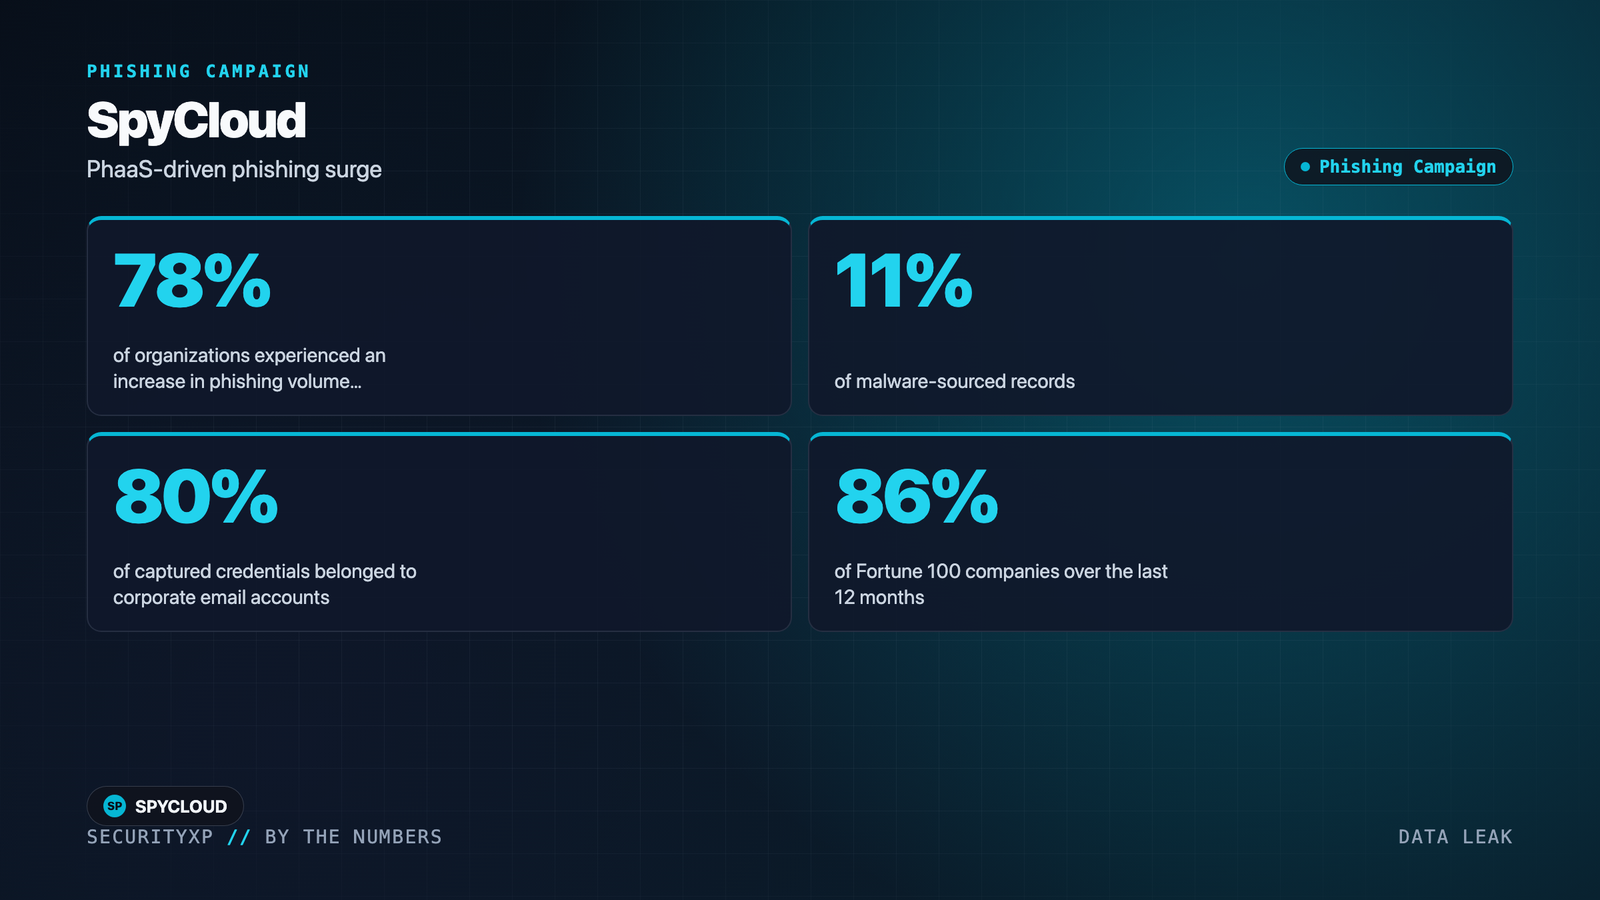
SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies
SpyCloud, the leader in identity threat protection, today released its 2026 Phishing Pulse Report, revealing that phishing attacks continue to increase in...