Author
SecurityXP
115 articles published · Page 2 of 6 RSS feed

SecurityXP delivers cybersecurity news, vulnerability analysis, data breach reports, and threat intelligence.
Articles
115 totalLLM Bridge Auditors Diagnose 60% of Vulnerable Source Inputs When Comments Remain
The arXiv paper 2611.21777, “LLMs as Validators for Cross-Chain Bridges: Evaluating Source-Level and Transaction-Level Attack Detection on Solana,” asks…
Optimizely Signup-Flow Vulnerability Injected Malicious JavaScript Into Sites of 178 Organizations
Optimizely confirmed that the attacker exploited a vulnerability in its Experimentation account signup flow.
Registry Gap: 65 Attacks Hit 305 Hospitals, 12 Drew No Breach Filing
At least 65 cyberattacks disrupted care at 305 U.S. hospitals since 2022; 12 older attacks have no federal breach-registry filing.
AuditTeam's 'Forced Audit': OpsAgent 5.2.8 Implant and Leak Site Behind the 'Audit & Consulting Fee'
AuditTeam entered the public record in March 2026, when open sources first identified the group via dbdigest.com.
Malicious Microsoft agent-framework Releases on PyPI Run a Credential Stealer on Every Python Start
Malicious versions of the Microsoft agent-framework PyPI package shipped a credential stealer that runs on every Python start, researchers found.
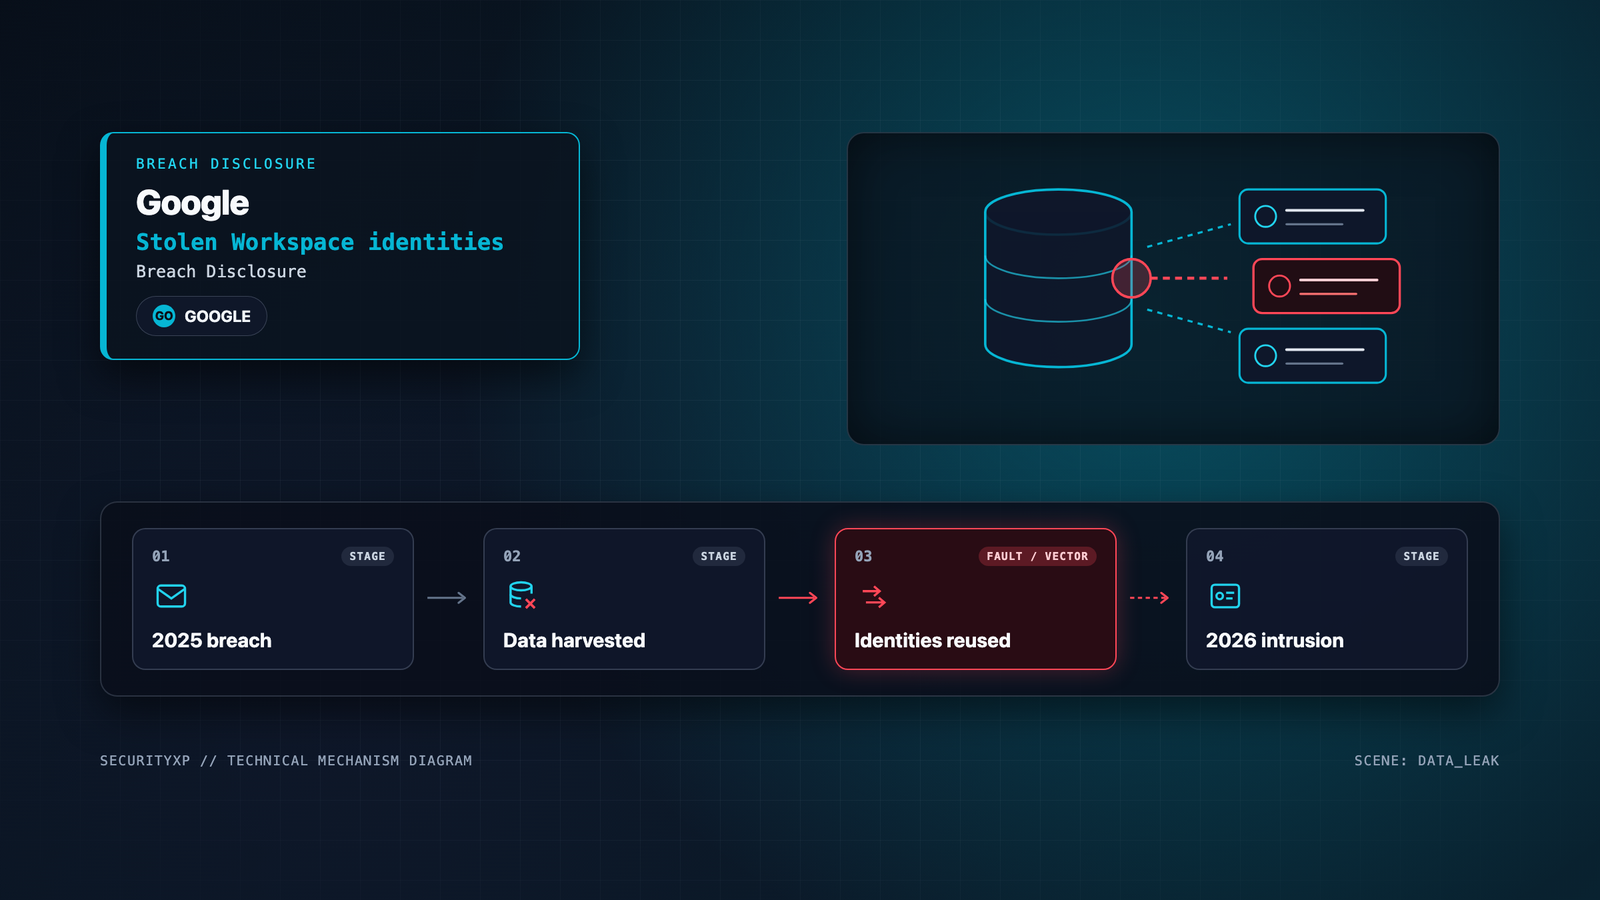
Cold Relic Reused Stolen Google Workspace Data to Breach a Second U.S. Organization
Google says Cold Relic reused stolen identities and Workspace data from an earlier breach to compromise a second U.S. organization.
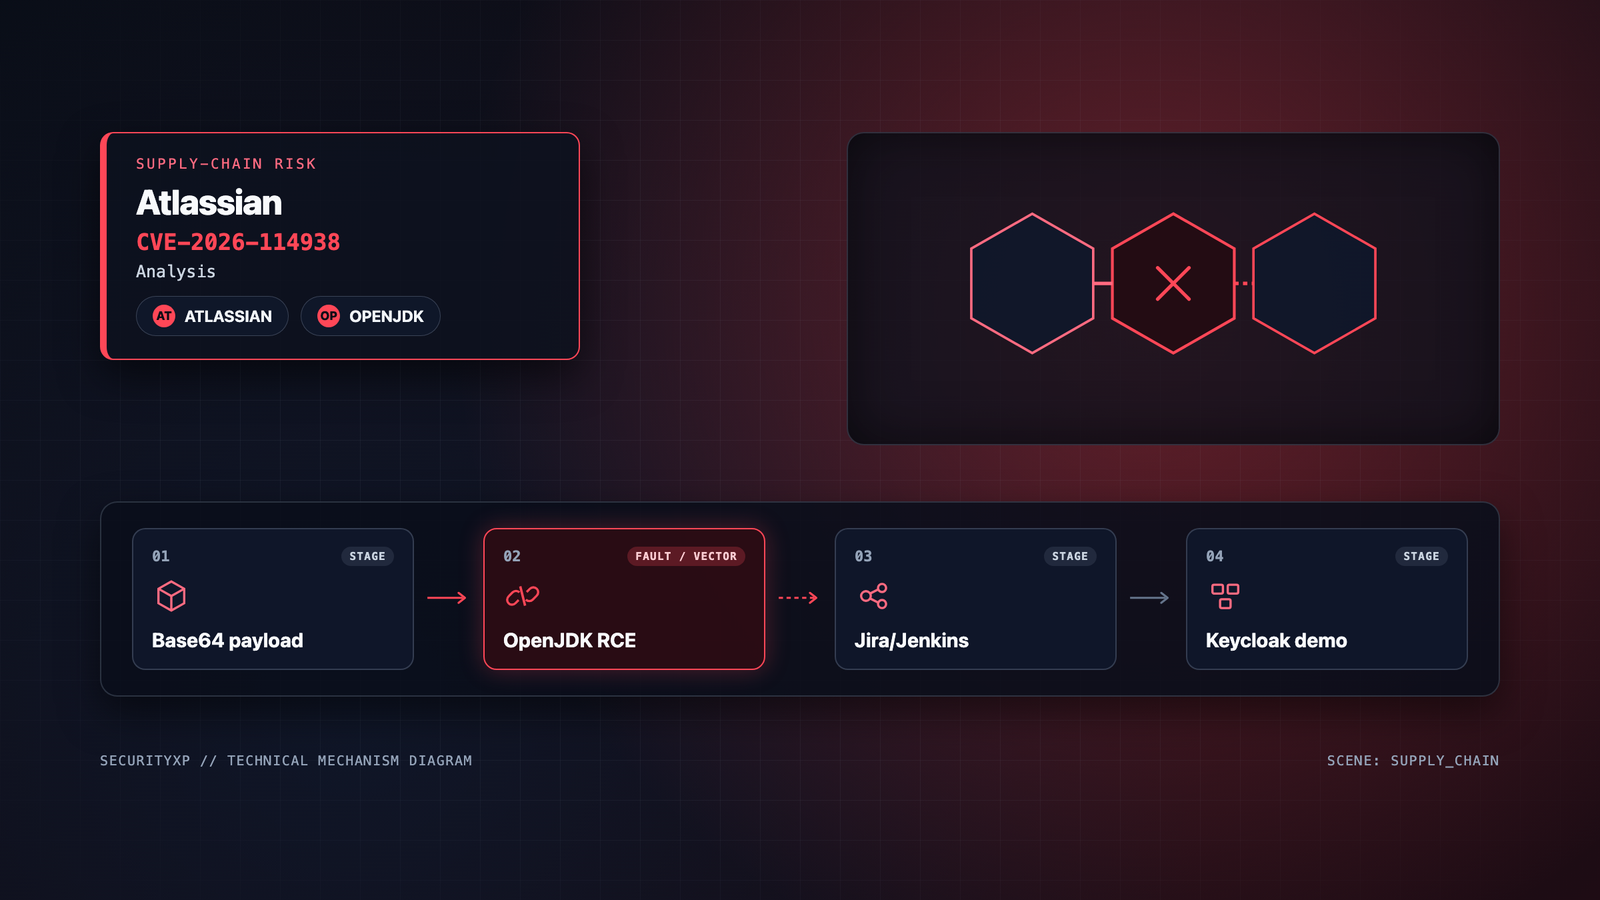
Java4Shell: What the CVE-2026-114938 Demonstrations in Jira, Jenkins and Keycloak Actually Show
JFrog and Semgrep analyses show how CVE-2026-114938 turns an OpenJDK Base64 decoder flaw into RCE — and CISA, Canada and Korea have issued urgent patch advisories.
Cisco Investigates Products After eMudhra Root CAs Distrusted Over Private Key Exposure
Cisco is auditing which products trust eight compromised eMudhra intermediate CAs and has published fixes and guidance for IOS XE, ASA, FMC and ISE.
ESLint's Payout Program Ended Over AI-Generated Code
ESLint ended its paid contributor program after AI-generated pull requests overwhelmed volunteer review capacity — a supply-chain integrity signal with downstream consequences.
Apache HTTP Server: Critical RCE Vulnerability (CVE-2026-119618)
Apache released HTTP Server 2.4.71 to fix CVE-2026-119618, a heap corruption flaw in mod_http2 that can lead to remote code execution. Affects Apache HTTP Server 2.4.55 through 2.4.70 with HTTP/2 enabled.
Citrix NetScaler ADC and Gateway: 28 Flaws, 2 Critical
CERT-EU advisory 2026-020: the Cloud Software Group published bulletins for 28 memory-safety flaws in Citrix NetScaler ADC and Gateway. CVE-2026-120868 (CVSS 9.3) affects all deployments including the default configuration.
Critical Vulnerability in Red Hat OpenShift AI (RHOAI) (CVE-2026-15378)
CVE-2026-15378 is a critical blind SSRF flaw in Red Hat OpenShift AI's guardrails-detectors component. A crafted XML Schema Definition string can make the server issue attacker-controlled requests. Red Hat rates it CVSS 9.3 and provides an official fix.
Dell BIOS Flaw Lets Attackers Recover Admin Passwords From SPI Flash in Milliseconds
Tracked as CVE-2026-40639 and addressed in Dell Security Advisory DSA-2026-197, the issue affects certain Dell client platforms that use the proprietary DVAR...
Weekly Metasploit Update: Exploits for FlowiseAI CSV Agent and MacOS Package Kit
Flowise CSV Agent Prompt Injection RCE Authors: Takahiro Yokoyama and zdi-disclosures Type: Exploit Pull request: 21407 contributed by Takahiro-Yoko Path...
Progress Urges ShareFile Admins to Shut Down Servers Over Credible Security Threat
In April 2026, watchTowr Labs disclosed two chainable vulnerabilities in Storage Zone Controller: CVE-2026-2699, an authentication bypass with a CVSS score...
WP-SHELLSTORM Exposed: Hackers Backdoored Thousands of WordPress Websites
Treat the Joomla JCE flaw (CVE-2026-48907, fixed in 2.9.99.5) as urgent too, since it is a maximum-severity and on CISA's actively-exploited list, even...
Cloudflare Signs the UK Government's Cyber Resilience Pledge
The UK's voluntary Cyber Resilience Pledge asks boards to own cyber risk and hold supply chains to a security baseline. Cloudflare has signed it. Here is what it asks for.
Critical Gitea Flaw Under Active Exploitation, Researchers Warn Vulnerability (CVE-2026-20896)
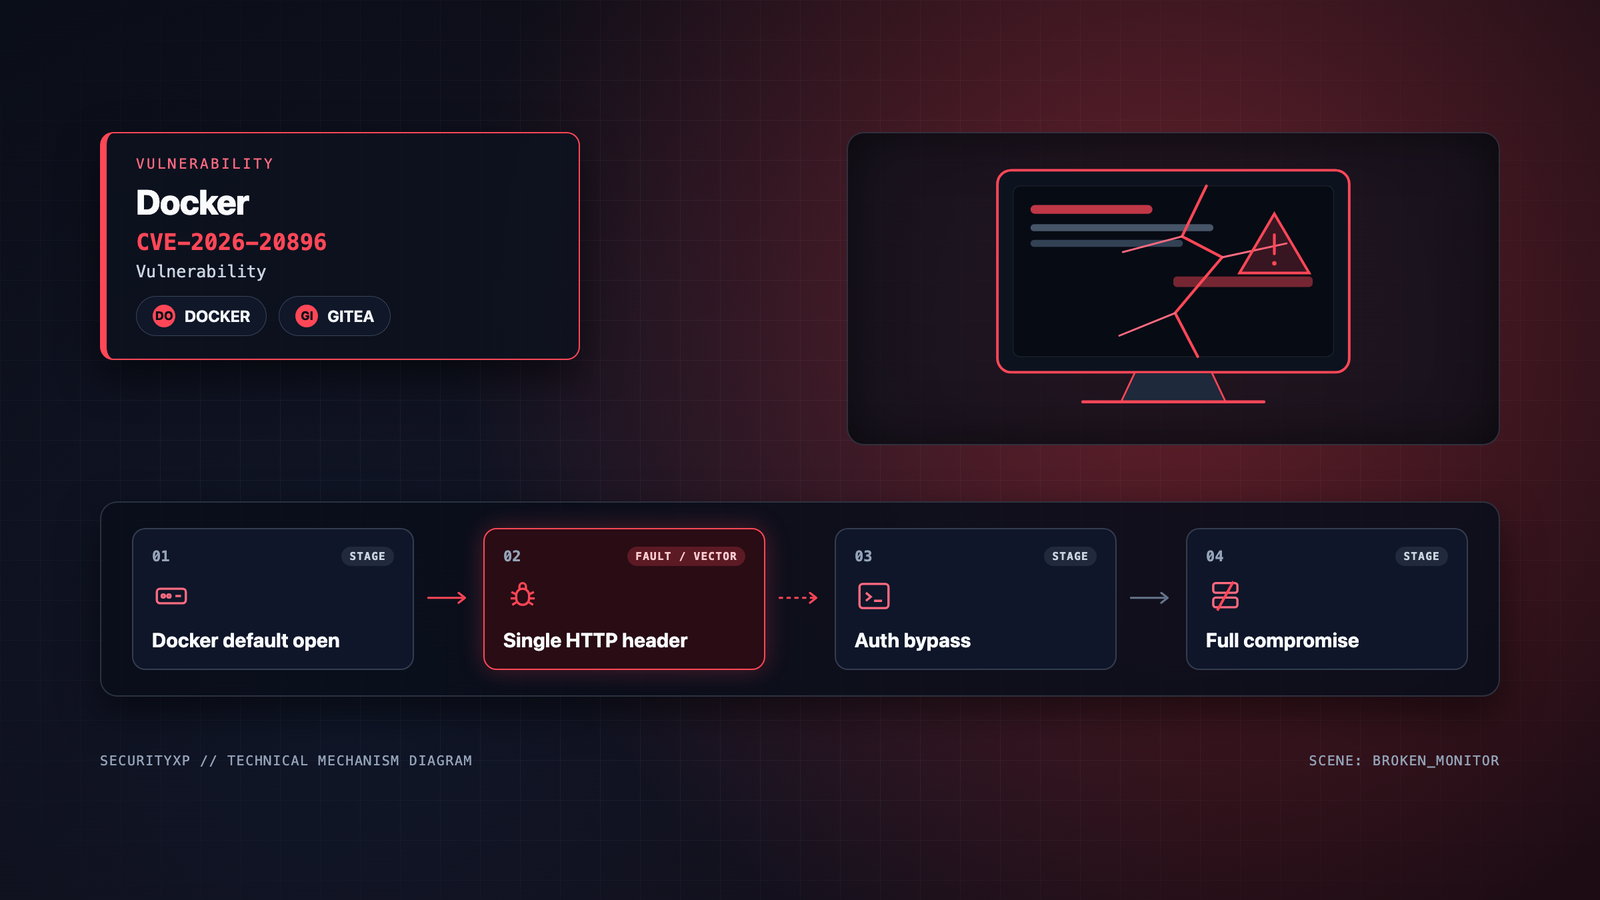
Specific to Gitea’s official Docker images, the critical-severity security defect is tracked as CVE-2026-20896 (CVSS score of 9.8) and can be exploited with...
Hitachi Energy e-mesh EMS Vulnerability (CVE-2026-42945)
The following versions of Hitachi Energy e-mesh EMS are affected: - Hitachi Energy e-mesh EMS 4.1.6, 4.4.2, 4.7.0 Background - Critical Infrastructure...
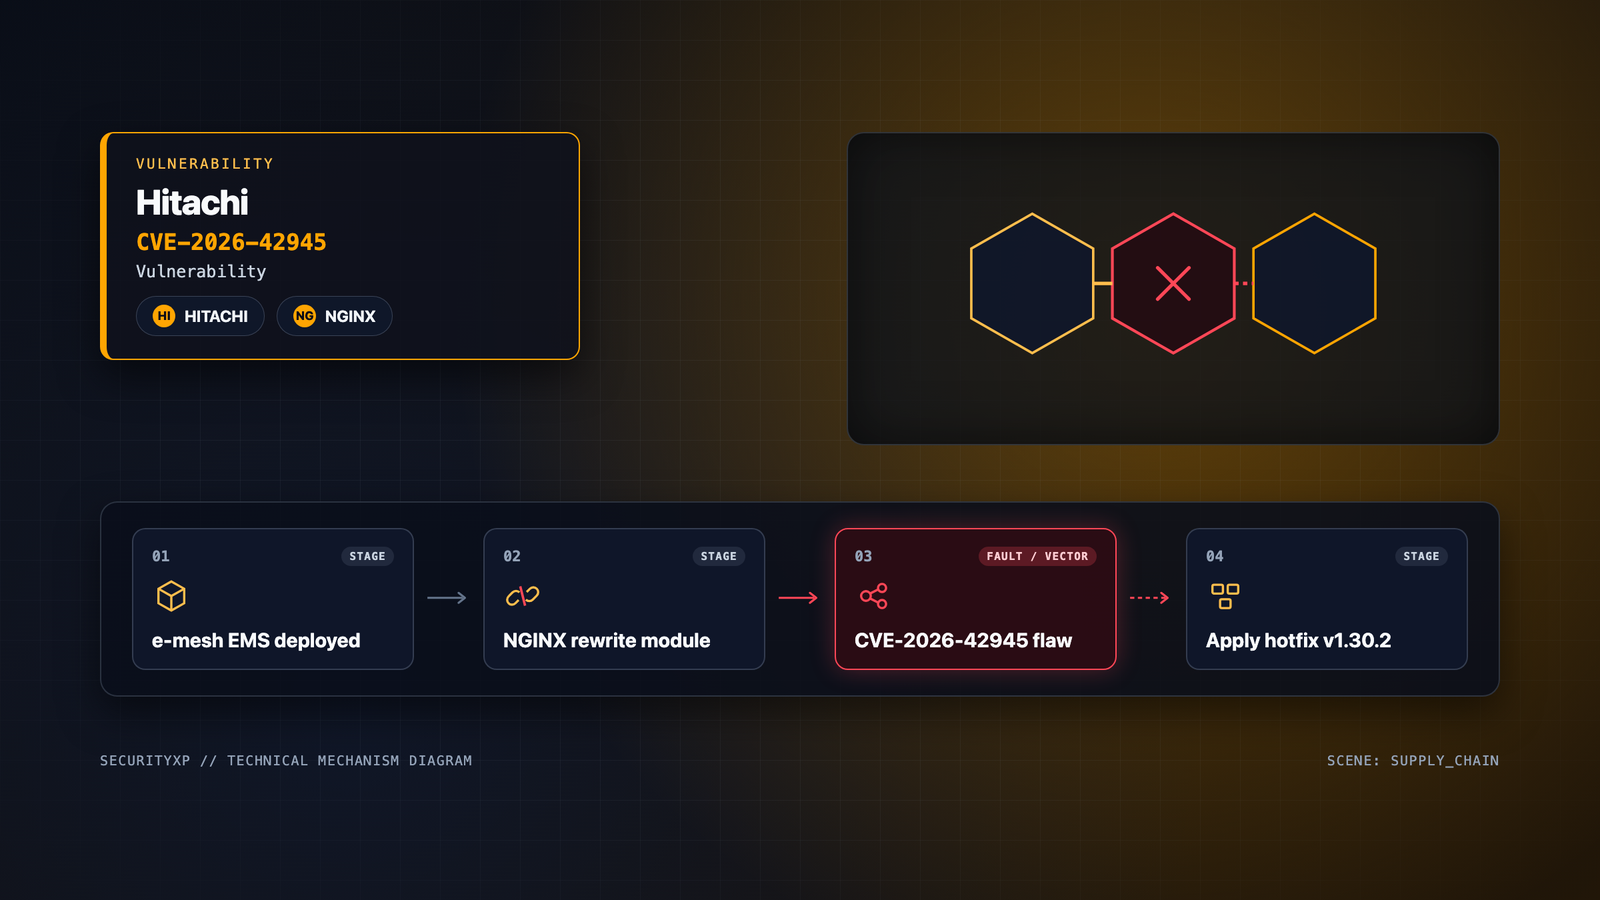
ABB launches FIM 3.5 with vendor-neutral automated firmware updates for industrial field devices
ABB announced launch of ABB Ability Field Information Manager (FIM) 3.5, a vendor-neutral platform for automated field device firmware updates. FIM 3.5...